10 Things Parents Are Overlooking About the Peachjar Data Leak
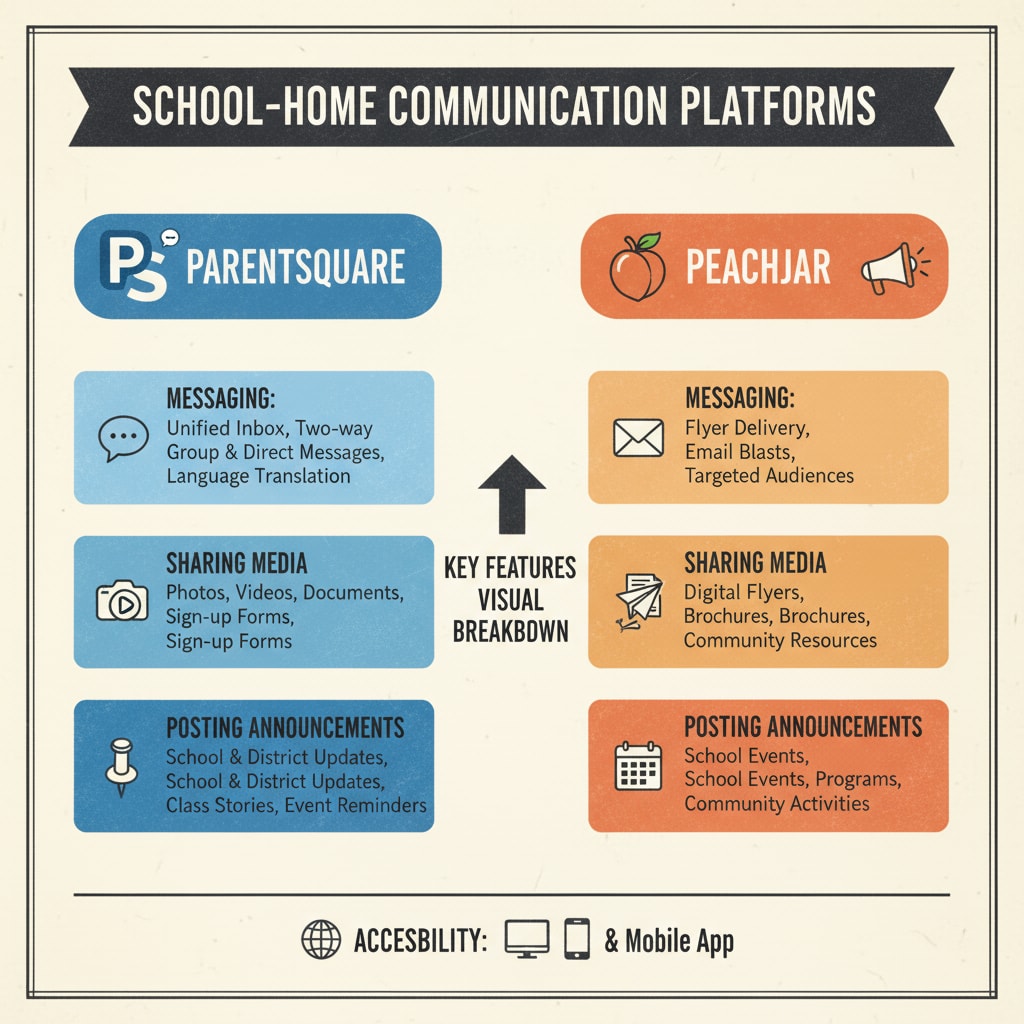
When digital flyers for school events, lunch menus, and after-school clubs arrive in your inbox, you rarely think about cybersecurity. For millions of families, Peachjar is the go-to platform for school communications. However, a significant security incident brought the platform into the headlines, raising alarms about family data privacy. While many families received generic notification emails about the incident, most have failed to grasp the full scope of the breach. There are several critical factors regarding the 10 Things Parents Are Overlooking About the Peachjar Data Leak that demand your immediate attention to safeguard your household.

Understanding the Scope of the Peachjar Incident
Data breaches involving educational technology platforms are uniquely concerning because they sit at the intersection of children's data and parental information. When a platform used by thousands of school districts suffers a compromise, the fallout extends far beyond standard corporate hacking incidents. Parents must look past the initial PR statements and examine the granular details of what was exposed.
1. The Exposure of Minor Data and Family Profiles
One of the most unsettling aspects of the Peachjar incident is the potential exposure of data linked to minor children. While platforms often claim to minimize children's data collection, account profiles frequently link parents, guardians, and students to specific schools, grade levels, and extracurricular interests. Malicious actors can compile these data points to build detailed dossiers on families.
2. Password Reuse and Credential Stuffing Risks
Many parents use the same password across multiple platforms, from school portals to online banking. If your Peachjar password was compromised, automated botnets will immediately test those exact credentials against your email, social media, and financial accounts. This practice, known as credential stuffing, is the primary way hackers turn a single minor data leak into a cascading financial disaster.
3. Phishing Attacks Tailored to Parents
Cybercriminals love context. Armed with the knowledge that you have a child in a specific school district, grade, and school, attackers can craft hyper-targeted phishing emails or text messages. An email pretending to be from your child's principal, the PTA, or Peachjar itself will look entirely legitimate because the sender knows your actual school district affiliation.
4. Outdated Account Information Is Still Valuable Data
A common mistake parents make is assuming that old accounts pose no risk. If your child graduated years ago or you moved to a different district, your old Peachjar profile sitting dormant in their database still contains historical home addresses, phone numbers, and email addresses. Stale data is frequently bundled and sold on dark web forums.
5. The False Sense of Security in "Educational" Apps
Parents naturally lower their guard when dealing with software approved or recommended by public school districts. There is an inherent assumption that school-affiliated vendors maintain bank-level security standards. The Peachjar data leak serves as a stark reminder that ed-tech vendors are often targeted precisely because their security is softer than major financial institutions.
Actionable Steps and Long-Term Vulnerabilities

Knowing that a breach occurred is only half the battle. Mitigating the fallout requires active defense, especially when dealing with platforms tied to your children's daily lives and institutional records.
6. Child Credit Freezes Are Urgently Needed
Most parents do not realize that minors can have credit reports. Identity thieves love targeting children because clean Social Security numbers can go unused for years without detection. While Peachjar may not collect full SSNs, aggregated data points can sometimes be cross-referenced with other leaked databases to compile complete profiles.
7. Third-Party App Permissions and Integrations
Did you sign up for Peachjar using your Google or Apple ID? Many parents overlook the third-party app permissions granted during registration. A data breach at a vendor level often means hackers can analyze how accounts were authenticated, potentially exposing tokens linked to your primary tech ecosystem.
8. The Risk of Secondary Data Brokering
Data collected by freemium or ad-supported school communication tools is frequently analyzed for marketing insights. When a database is leaked, that information escapes its original corporate ecosystem. Your family's demographic details, school district, and inferred spending habits may now reside in unverified data broker hands.
9. Inadequate Notification Timelines
State laws regarding data breach notifications vary wildly, and educational vendors often operate in regulatory gray areas. Many parents learned about the incident long after hackers accessed the servers. Relying solely on corporate notifications leaves families vulnerable during the critical window immediately following a cyberattack.
10. The Need for a Family Digital Hygiene Reset
The ultimate takeaway from this incident is that modern parenting requires proactive digital hygiene. Families must adopt password managers, enable multi-factor authentication (MFA) on every active account, and regularly audit which school apps retain active permissions to personal data.
Protecting Your Family Moving Forward
Data leaks have become an unfortunate reality of the modern digital landscape, but you are not powerless. By recognizing that the Peachjar data leak goes beyond a simple administrative hiccup, you can take concrete steps to secure your digital perimeter. Reset your passwords, monitor your email for suspicious communications, and treat every school-related platform with the same security awareness you apply to your bank accounts.