Evawxsh Leaks: Timeline & Expert Opinions
In the fast-paced world of digital media and cybersecurity, few incidents capture public and professional attention quite like major data breaches. Recently, discussions surrounding the Evawxsh leaks have dominated technology forums, news outlets, and social media platforms. Beyond the initial shock value of the leaked materials, the incident has sparked widespread debate among cybersecurity professionals, legal experts, and privacy advocates. Understanding the gravity of this event requires looking past the headlines and examining the chronological progression of the breach, alongside professional assessments of what went wrong.
Expert Opinions on the Evawxsh Leaks: A Timeline of Events
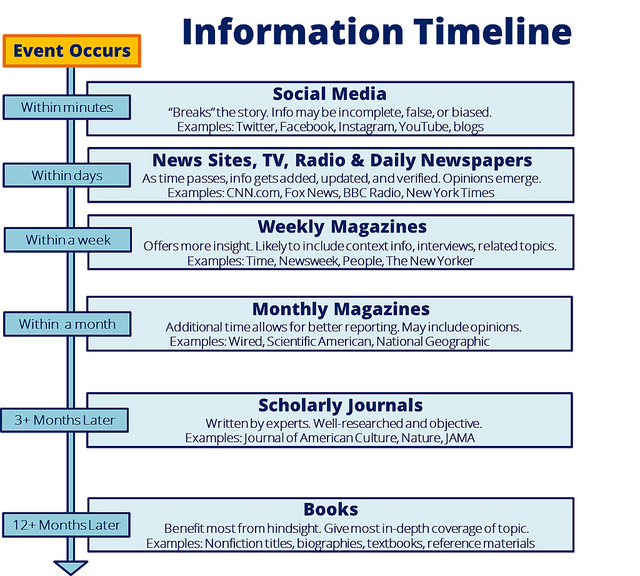
To fully grasp the scope of the incident, we must trace how the situation unfolded from its initial rumblings to a full-scale digital crisis. Industry analysts and forensic investigators have pieced together the following sequence of events, shedding light on the vulnerabilities exploited and the subsequent fallout.
Phase 1: The Initial Rumblings and Discovery
The story began quietly on niche online forums and decentralized chat applications. Security researchers first noticed anomalous data traffic and unauthorized access attempts targeting endpoints associated with Evawxsh. During this initial phase, the scale of the potential exposure was largely unknown, and internal teams scrambled to verify whether a legitimate breach had occurred.
- Day 1-2: Unusual data packets detected by third-party threat intelligence monitors.
- Day 3: Preliminary internal audits confirm unauthorized extraction of proprietary information.
- Day 4: First public mentions appear on social media platforms, driven by data-leak watchdogs.
Phase 2: Public Disclosure and Rapid Escalation
As verifiable snippets of the compromised data began circulating publicly, the situation shifted from an internal security concern to a major public relations and compliance crisis. Media outlets picked up the story, and the term 'Evawxsh leaks' quickly trended globally. At this point, cybersecurity experts stepped in to analyze the authenticity and classification of the exposed files.
According to digital forensics specialists, the attackers utilized sophisticated credential-stuffing techniques combined with social engineering to bypass perimeter defenses. This revelation shifted the conversation from a simple software bug to a broader failure in multi-factor authentication (MFA) enforcement and employee security training.
Phase 3: Containment, Damage Control, and Response
Once the breach was fully acknowledged by stakeholders, emergency incident response protocols were enacted. Servers were temporarily taken offline for sanitization, and enterprise security partners were brought in to conduct root-cause analyses.

- Revocation of all compromised API keys and administrative credentials.
- Deployment of advanced endpoint detection and response (EDR) agents across all networks.
- Issuance of formal transparency reports to affected users and regulatory bodies.
Cybersecurity Expert Analysis and Takeaways
Security analysts reviewing the Evawxsh leaks have emphasized several critical lessons for modern organizations. The incident serves as a stark reminder that no digital ecosystem is entirely immune to targeted attacks, regardless of its size or sophistication.
The Human Element in Security Failures
A recurring theme in expert commentary is the role of human error. While technical vulnerabilities are often blamed, the initial breach vector frequently traces back to phishing or compromised credentials. Analysts stress that technical safeguards must be paired with continuous, engaging employee awareness programs to drastically reduce susceptibility to social engineering.
Regulatory and Compliance Repercussions
Legal and compliance experts point out that the fallout extends far beyond reputational damage. Depending on the geographical distribution of the affected users, organizations face stringent scrutiny under data protection frameworks like GDPR and CCPA. Failure to notify authorities and impacted individuals within mandated timeframes can result in severe financial penalties.
Looking Forward: Preventing Future Incidents
The aftermath of the Evawxsh leaks highlights the necessity of adopting a Zero Trust architecture. Industry leaders argue that perimeter security is dead; organizations must operate under the assumption that networks are already compromised. By implementing micro-segmentation, continuous behavior monitoring, and rigorous access controls, businesses can contain potential breaches before they escalate into catastrophic data leaks.
Ultimately, the incident will be studied in cybersecurity classrooms for years to come. It underscores the vital balance between rapid digital innovation and robust, proactive defense strategies in an increasingly hostile threat landscape.