Inside Finnster leaks: 4 At-Risk US Data Industries
Understanding the Finnster Leaks and US Data Security
In the rapidly evolving landscape of cybersecurity, high-profile data breaches continually test the resilience of modern digital infrastructure. Recently, discussions surrounding the inside Finnster leaks have brought renewed attention to how unauthorized data exposure impacts organizations across the United States. While public fascination often centers on the sensational aspects of data dumps, cybersecurity professionals look deeper at the systemic vulnerabilities that allow sensitive information to leak in the first place.
When large-scale datasets are compromised, the ripple effects extend far beyond immediate privacy violations. They expose structural weaknesses in how enterprises collect, store, and manage information. To understand the true gravity of these incidents, we must examine the specific sectors where digital assets are most heavily concentrated and, consequently, where the risks of stolen US data are highest.
The 4 Industries at Highest Risk from Stolen US Data
Data is the lifeblood of the modern economy, but not all data holds equal value to malicious actors. Certain sectors handle massive volumes of sensitive, regulated, or proprietary information, making them prime targets for cybercriminals. Following major incidents like the inside Finnster leaks, security analysts have identified four key industries facing the most severe exposure risks.
1. Healthcare and Medical Research
The healthcare sector remains a primary target for data theft due to the immense monetary and operational value of Protected Health Information (PHI). Medical records contain a treasure trove of personally identifiable information (PII), including Social Security numbers, home addresses, insurance details, and detailed medical histories.
Unlike credit card numbers, which can be easily cancelled and replaced, a person's medical history is permanent. This makes healthcare data exceptionally valuable on underground forums. Furthermore, many medical institutions operate on legacy software systems that lack advanced endpoint detection and response tools, leaving them uniquely vulnerable to sophisticated intrusion campaigns and subsequent data leaks.
2. Financial Services and Banking
Financial institutions are perpetual targets for cyberattacks, but the nature of the risk has shifted. Beyond direct bank heists, modern threat actors focus on stealing non-public financial information, algorithmic trading secrets, and comprehensive customer databases.
- Identity Theft Risks: Stolen consumer financial records enable complex synthetic identity fraud.
- Regulatory Penalties: Breaches trigger severe compliance fines from bodies like the SEC and FINRA.
- Reputational Damage: Loss of client trust can permanently erode a financial institution's market share.
Incidents that highlight vulnerabilities in data handling remind banks that perimeter defense is no longer enough; robust internal data governance and encryption are mandatory.

3. Government and Defense Contractors
The public sector and its vast web of private contractors hold some of the most sensitive secrets in the nation, ranging from intellectual property regarding military hardware to classified citizen databases. State-sponsored hackers and financially motivated cyber syndicates alike target these entities to gain strategic advantages or leverage for extortion.
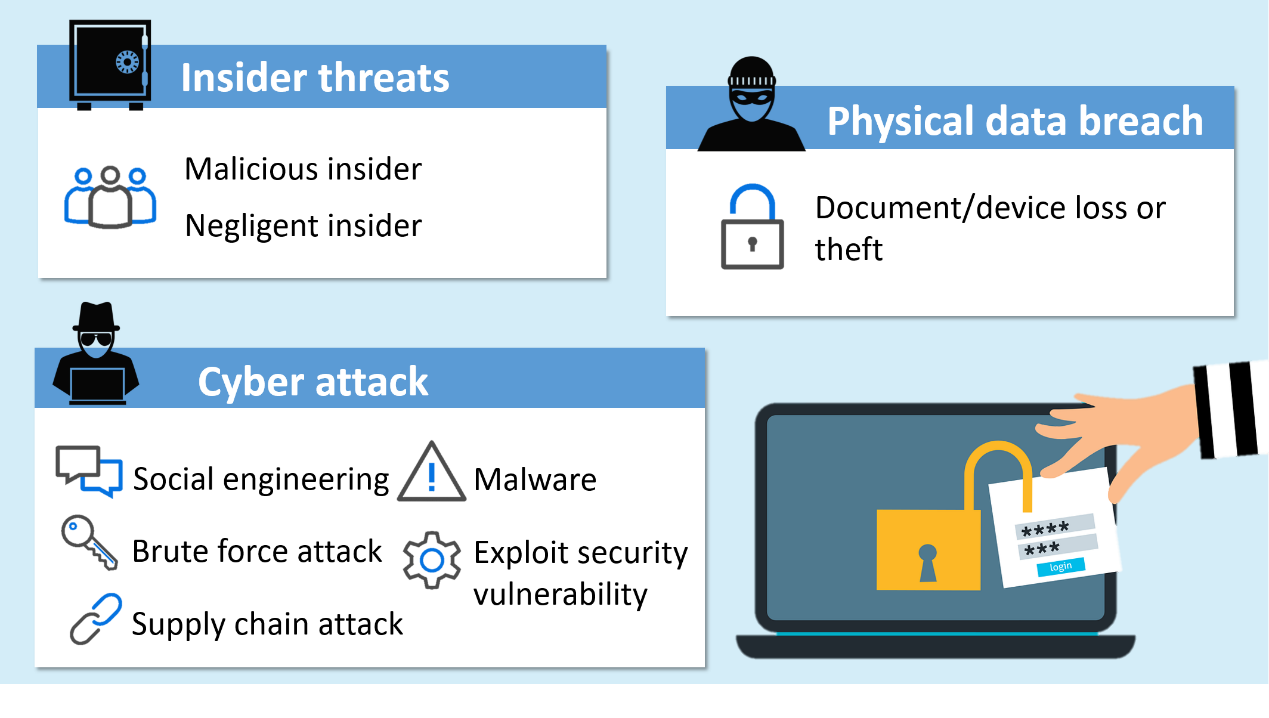
Because defense supply chains often involve numerous small-to-medium-sized subcontractors with varying levels of cybersecurity maturity, attackers frequently use these third-party vendors as stepping stones to breach larger federal networks. Securing the defense industrial base against data exfiltration has thus become a top national security priority.
4. Technology and SaaS Providers
Software-as-a-Service (SaaS) providers and technology firms sit at the center of the modern digital ecosystem. They store source code, intellectual property, and credential databases for thousands of downstream business clients. A single successful breach against a major tech provider can cascade into a massive supply chain attack, exposing data across multiple unrelated industries.
As remote work environments and cloud migrations expand the digital attack surface, tech companies must adopt zero-trust architectures. Protecting API endpoints and implementing strict access controls are essential steps to prevent the unauthorized extraction of proprietary source code and user credentials.
Mitigating Modern Data Exfiltration Risks
The lessons learned from incidents like the inside Finnster leaks underscore a universal truth: traditional perimeter security is obsolete. Organizations across all sectors must transition toward a proactive security posture focused on resilience rather than mere prevention.
Key Defense Strategies for Enterprises
- Data Minimization: Collect and retain only the data that is strictly necessary for business operations. The less data you store, the smaller your attack surface.
- End-to-End Encryption: Ensure sensitive data is encrypted both in transit and at rest, making stolen information useless to unauthorized parties.
- Continuous Monitoring: Deploy behavioral analytics and AI-driven monitoring tools to detect anomalous data exfiltration attempts in real time.
- Employee Training: Conduct regular phishing simulations and security awareness programs to mitigate the human error factor that often precipitates a breach.
Ultimately, safeguarding sensitive information requires a cultural shift within organizations. By treating data security as a core business function rather than an IT afterthought, companies can better insulate themselves against the escalating threats highlighted by modern data leaks.