Inside the Breach Lens: Viptoria's Cyber Incident
Decoding Modern Cyber Warfare

In the digital age, cybersecurity incidents are a daily occurrence, ranging from minor phishing attacks to sophisticated supply chain compromises. However, rare events fundamentally alter how organizations perceive risk. When analysts look Inside the Breach Lens: Why Viptoria’s Leaks Became the Greatest Cyber Incident Yet, they see more than just stolen data. They see a watershed moment that exposed the fragile underbelly of modern interconnected enterprise systems.
The Viptoria breach was not merely a database theft; it was a masterclass in persistent, multi-layered infiltration. The attackers bypassed traditional perimeter defenses, moved laterally across cloud environments, and exfiltrated terabytes of proprietary source code, internal communications, and zero-day vulnerability stockpiles. To understand why this event stands apart in cybersecurity history, we must dissect the anatomy of the attack and its cascading global effects.
The Anatomy of the Viptoria Breach
Every major cyber incident leaves a trail of technical indicators that forensic investigators piece together. The Viptoria incident began months before public disclosure, utilizing a combination of novel attack vectors and human error.
Initial Access and Zero-Day Exploitation
The threat actors did not rely on standard credential stuffing or generic phishing campaigns. Instead, they weaponized a zero-day vulnerability in Viptoria’s edge-gateway routing appliances. This allowed them to establish a quiet, encrypted foothold inside the corporate network without triggering legacy intrusion detection systems (IDS).
- Bypassed multifactor authentication (MFA) via session-hijacking techniques.
- Leveraged compromised service accounts with over-permissioned administrative privileges.
- Utilized living-off-the-land (LotL) binaries to blend malicious activities with legitimate administrative traffic.
Lateral Movement and Credential Harvesting
Once inside, the attackers maintained a low profile while mapping the internal architecture. They targeted the company’s identity provider, gaining access to master keys and certificate authorities. This level of access meant the intruders could move through the network disguised as trusted entities, rendering standard segmentation strategies largely ineffective.
Why Viptoria’s Leaks Changed the Threat Landscape
Security analysts frequently debate which cyber event deserves the title of 'worst in history.' While older breaches involved larger volumes of consumer records, the Viptoria incident is unique due to the nature and sensitivity of the leaked assets.
Exposure of Critical Infrastructure Blueprints

Unlike retail breaches that expose credit card numbers or names, the Viptoria leaks compromised the foundational software libraries used by thousands of downstream enterprise clients. This created a domino effect, turning a single corporate breach into a systemic supply chain emergency.
The Psychological and Economic Impact
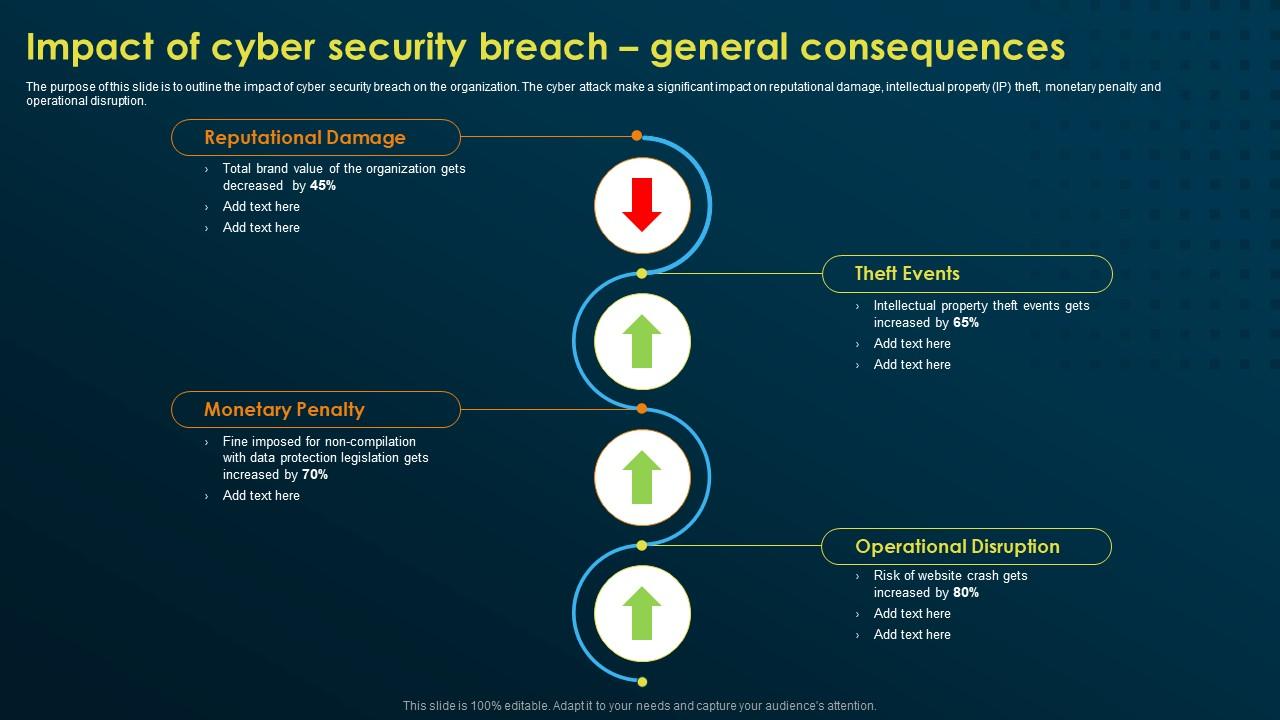
The public release of internal executive communications damaged trust and triggered immediate regulatory scrutiny from international privacy watchdogs. Furthermore, the publication of proprietary algorithms meant competitors—and hostile nation-states—gained immediate insight into Viptoria's intellectual property, wiping billions off its market valuation within days of the disclosure.
Key Lessons for Enterprise Security
Organizations across all sectors must adapt their defensive postures in light of the tactics observed during the Viptoria incident. Relying on compliance checklists is no longer sufficient to stop advanced persistent threats (APTs).
Embracing Zero Trust Architecture
The assumption of implicit trust inside a corporate network is a fatal flaw. A robust Zero Trust model enforces continuous verification of every user and device, regardless of whether they are located inside or outside the physical perimeter.
Enhancing Supply Chain Visibility
Third-party software vendors represent one of the most significant vectors for modern attacks. Enterprises must demand rigorous security transparency from their partners, conducting independent software bill of materials (SBOM) audits and continuous vendor risk assessments.
Conclusion
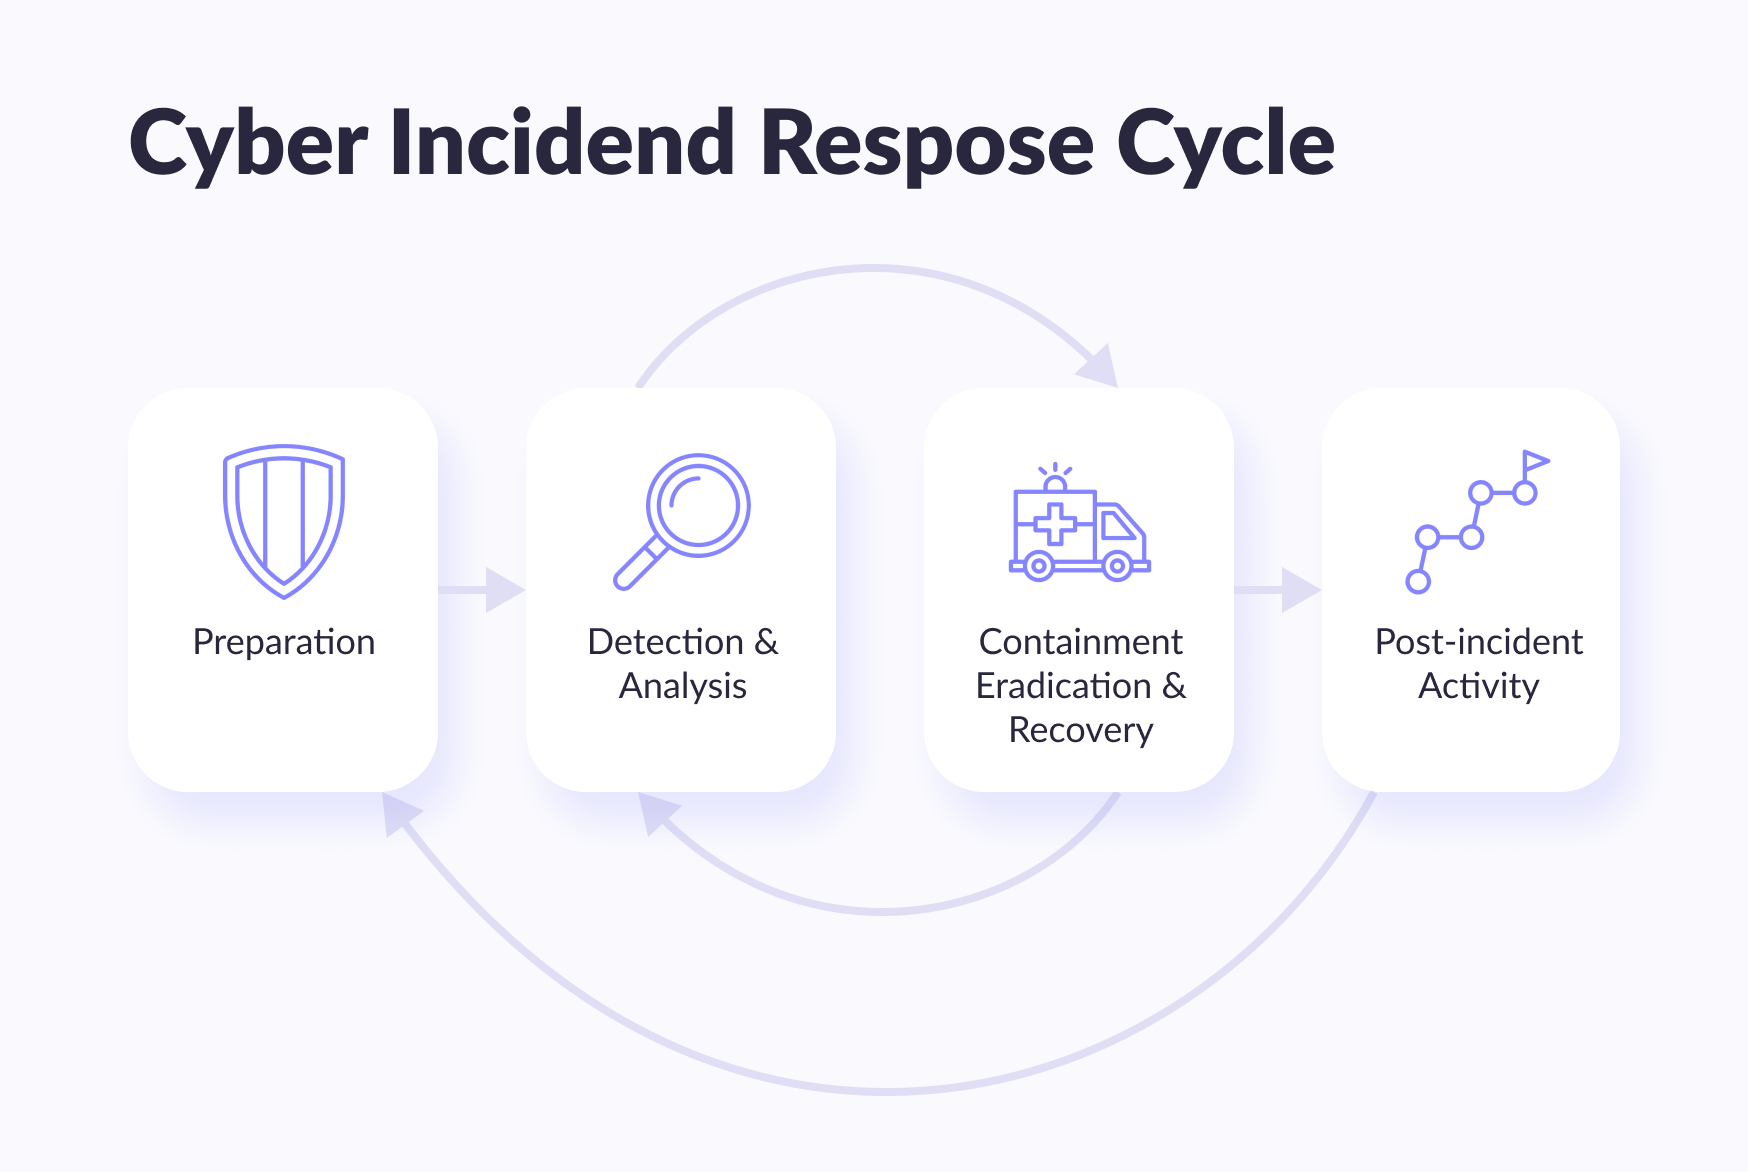
The fallout from the Viptoria incident continues to reverberate through boardrooms and security operations centers worldwide. By examining the event through a critical lens, organizations can better prepare for the next generation of cyber threats. The era of perimeter defense is officially over; resilience now depends on visibility, rapid containment, and absolute zero-trust execution.