Inside the ImaubreyKeys Leak: Data Security Guide
Understanding the ImaubreyKeys Leak

In the fast-paced world of digital media and online content creation, high-profile security incidents can happen with alarming frequency. Recently, attention has turned toward the digital footprint of prominent figures and online personalities, bringing events like the Inside the ImaubreyKeys Leak – What It Really Means for Your Data Security discussion to the forefront of cybersecurity forums. While celebrity and influencer data breaches often dominate headlines for their sensationalism, they offer critical technical lessons for everyday internet users.
When a prominent online handle or creator experiences a security compromise, it rarely happens in a vacuum. These events typically expose vulnerabilities that affect not just the individual, but also the broader ecosystem of platforms, third-party apps, and credential management systems. By examining the anatomy of these incidents, we can move past the gossip and focus on actionable takeaways for personal cybersecurity.
How High-Profile Leaks Actually Happen
Security breaches rarely involve a Hollywood-style hacker guessing passwords on a glowing terminal. Instead, they usually exploit predictable weak points in human behavior or software architecture. Understanding these vectors is the first step toward building an effective defense strategy for your own digital assets.
Credential Stuffing and Reuse
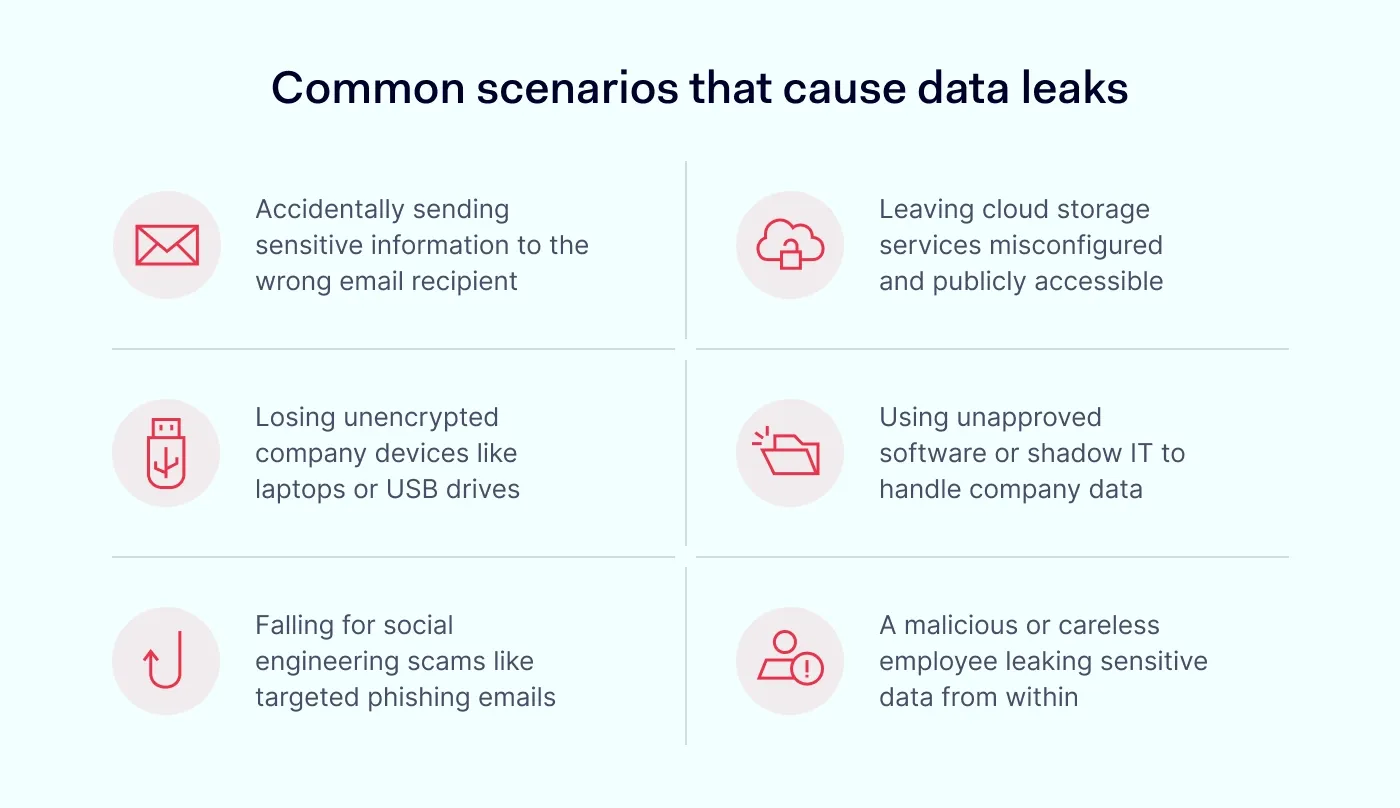
One of the most common catalysts for digital leaks is credential reuse. Many users utilize the same password across multiple platforms for the sake of convenience. When a low-security website suffers a data breach, automated bots quickly test those leaked email-and-password combinations against higher-value platforms like social media accounts, cloud storage, and email providers. If a creator reused a password, a breach elsewhere can easily translate into a targeted account takeover.
Phishing and Social Engineering
Online creators and influencers are prime targets for sophisticated phishing campaigns. Attackers frequently pose as brand sponsors, collaboration partners, or platform support teams. By sending convincing emails or direct messages containing malicious links, bad actors can trick victims into surrendering login credentials, two-factor authentication (2FA) codes, or API tokens. Once inside, attackers can harvest private archives and personal data in minutes.
Third-Party App Integration Risks
Modern platforms rely heavily on third-party integrations to schedule posts, analyze audience metrics, and manage communities. Granting OAuth access to poorly audited applications creates hidden backdoors. If a third-party developer suffers a database leak, malicious actors may gain sweeping permissions to read, write, or download private data from connected user accounts without the owner ever realizing it.
The Broader Implications for Everyday Users
It is easy to assume that high-profile digital exposures only matter if you are a public figure. However, the technical lessons learned from incidents like the ImaubreyKeys exposure apply universally. Cybercriminals do not just target fame; they target data monetization, extortion, and identity theft.

- Monetization of Private Data: Stolen content, private messages, and personal credentials command high prices on underground forums, motivating automated attacks against accounts of all sizes.
- Identity Theft Risks: Personal information exposed during a breach can be compiled into detailed dossiers, enabling scammers to impersonate victims for financial fraud or social engineering attacks against friends and family.
- Reputational Damage: A compromised account can be weaponized to spread spam, malware, or offensive material, causing severe damage to personal or professional reputations before the platform can intervene.
Actionable Steps to Harden Your Digital Security
You cannot control platform security or prevent third-party databases from getting hacked, but you can dramatically reduce your personal attack surface. Implementing a robust defense posture requires shifting from reactive scrambling to proactive hygiene.
1. Adopt a Zero-Trust Password Strategy
Stop memorizing passwords. Utilize a reputable, encrypted password manager to generate and store unique, complex passwords for every single account you own. This ensures that a breach on an obscure forum account will never jeopardize your primary email or social profiles.
2. Upgrade to Hardware-Based Multi-Factor Authentication
Standard SMS-based two-factor authentication is vulnerable to SIM-swapping and interception attacks. Whenever possible, secure your accounts using authenticator apps (like Aegis or Google Authenticator) or physical hardware security keys (such as YubiKeys). Hardware keys offer the highest level of phishing resistance available today.
3. Audit Connected Apps and Permissions
Take twenty minutes today to review the settings on your major Google, Apple, social media, and financial accounts. Revoke access for any third-party websites, games, or applications that you no longer actively use or recognize.
4. Practice Digital Minimalism
Remember that the safest data is the data you never store online. Regularly purge old chat logs, delete unnecessary cloud backups, and be mindful of what personal details you share across public and semi-private platforms.
Conclusion
Incidents involving digital exposures and account compromises will continue to make headlines as our lives move increasingly online. Rather than viewing these events as isolated celebrity drama, use them as a timely reminder to audit your own defenses. By upgrading your password hygiene, implementing strong multi-factor authentication, and minimizing your digital footprint, you can ensure that your personal data remains secure against evolving online threats.