JaliNe Ojeda’s Secret Files: Breach Impact Explained
In the digital age, a single data leak can cascade through corporate networks, government agencies, and public utilities in a matter of hours. The recent discussion surrounding JaliNe Ojeda’s Secret Files: Why This Breach Triggers Systems Across the US has captured the attention of cybersecurity experts, compliance officers, and everyday internet users alike. Rather than being just another isolated celebrity gossip item, this incident highlights deep structural flaws in modern cloud storage, credential management, and third-party data handling.

Understanding the Incident
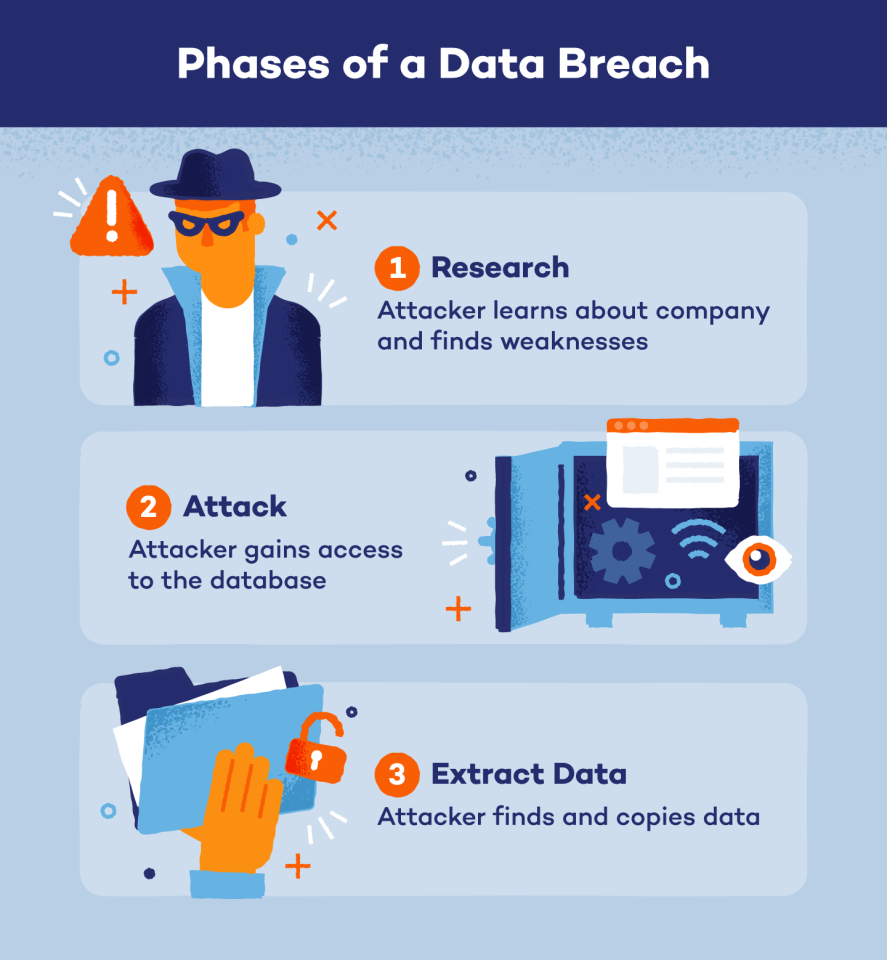
Data breaches rarely happen in a vacuum. When sensitive repositories—often referred to colloquially or specifically in leaks as JaliNe Ojeda’s secret files—suddenly appear on forums or private cloud buckets, it usually points to a sophisticated social engineering attack, a misconfigured cloud storage bucket, or compromised administrative credentials.
Security analysts tracking the event noted several key vectors:
- Exposed Cloud Buckets: Misconfigured permissions allowing public read-access to sensitive repositories.
- Credential Stuffing: Attackers utilizing leaked password lists from previous database compromises to gain initial access.
- Third-Party Vendor Access: Exploitation of supply chain partners who maintained lower security postures while holding integration privileges.
Why This Breach Triggers Systems Across the US
The phrase "triggers systems across the US" is not merely hyperbole; it reflects the automated safeguards and interconnected nature of modern enterprise networks. When high-profile data sets leak, automated Threat Intelligence Platforms (TIPs) and Intrusion Detection Systems (IDS) immediately scan for matching cryptographic hashes, IP traffic patterns, and credential footprints.
The Cascade Effect on Corporate Networks
Modern businesses rely heavily on interconnected software-as-a-service (SaaS) platforms. If a user whose data appears in these files utilized the same corporate email and password combination for workplace software, automated Security Information and Event Management (SIEM) tools instantly flag the anomaly.
Consequently, IT departments nationwide initiate automated lockouts, force password resets, and audit access logs. This defensive reaction consumes thousands of man-hours and temporarily disrupts routine business operations across multiple sectors.
Regulatory and Compliance Alarms
Data protection frameworks such as the California Consumer Privacy Act (CCPA) and various sectoral regulations mandate rapid incident response and notification procedures. The widespread visibility of these files forces legal and compliance teams to evaluate whether personally identifiable information (PII) has been compromised, triggering mandatory reporting obligations to state and federal agencies.
Lessons for Individuals and Organizations
Every major security event provides a blueprint for hardening defenses. Whether you are an enterprise security architect or an individual looking to safeguard your digital footprint, the fallout from these exposed files offers critical takeaways.
1. Mandatory Multi-Factor Authentication (MFA)
Passwords alone are no longer sufficient. Implementing phishing-resistant MFA—such as hardware security keys or authenticator apps—drastically reduces the likelihood of unauthorized account takeover, even if underlying credentials are leaked.
2. Continuous Cloud Auditing
Organizations must deploy automated posture management tools to continuously inspect cloud environments (AWS S3, Azure Blob, Google Cloud Storage) for accidental public exposure settings.
3. Zero-Trust Architecture
Moving away from perimeter-based security toward a Zero-Trust model ensures that even if a bad actor breaches one segment of a network, lateral movement is severely restricted by continuous verification protocols.
Conclusion
The conversation surrounding JaliNe Ojeda’s secret files goes far beyond the immediate shock value of the leaked content. It serves as a stark reminder of how fragile digital ecosystems can be when hygiene standards slip. By understanding why these incidents trigger widespread defensive measures, organizations and individuals can better prepare for the inevitable challenges of the modern threat landscape.


.webp)