Knee Abrasion ICD 10 and Cybersecurity
Introduction to Clinical Data and Digital Defense

At first glance, a minor clinical diagnosis and digital infrastructure security appear to inhabit entirely different universes. One belongs in the domain of scraped skin, antiseptic wipes, and physical triage, while the other is governed by firewalls, encryption keys, and threat intelligence feeds. Yet, in the modern healthcare ecosystem, every patient encounter leaves a digital footprint. Understanding **the connection between knee abrasion ICD 10 code and healthcare cybersecurity services development** reveals how fundamental administrative data shapes the security protocols protecting our most sensitive health records.
As hospitals and clinics digitize their workflows, medical billing, diagnostic coding, and patient management systems become tightly integrated. This digital transformation improves care coordination but also expands the attack surface for malicious actors. To appreciate why a simple skin scrape matters to cybersecurity architects, we must examine how clinical data flows through digital networks and why it requires robust protection.
The Anatomy of Medical Data Generation
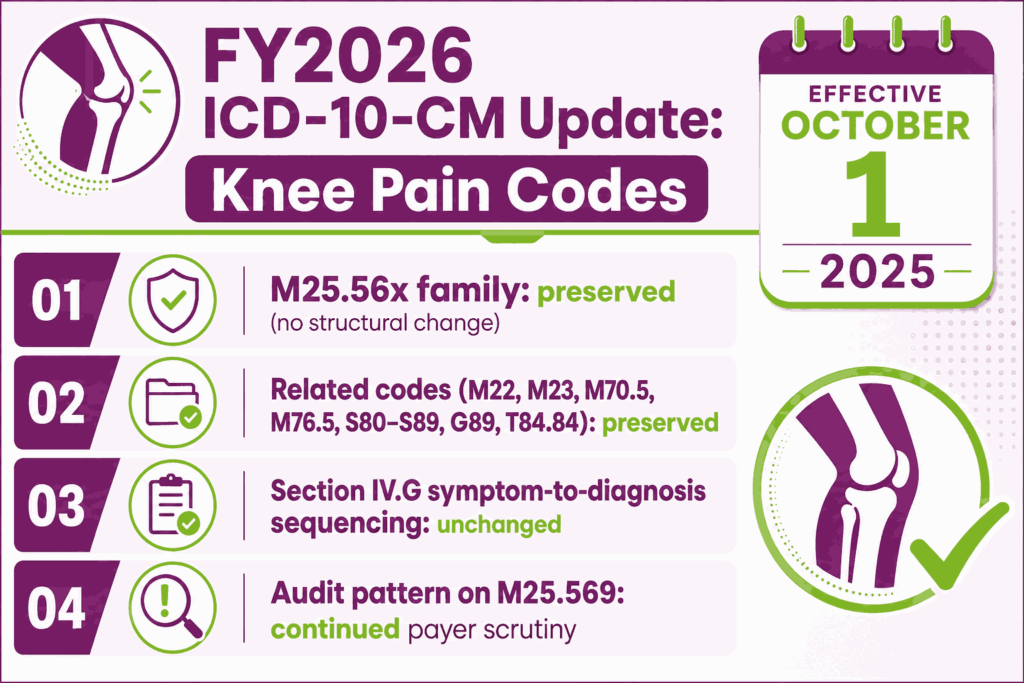
When a patient visits an emergency room or outpatient clinic with a scraped knee, a specific administrative workflow begins. Clinicians examine the injury, clean the wound, and document the encounter in an Electronic Health Record (EHR) system. To ensure proper reimbursement and standardized epidemiological tracking, medical coders translate the clinical notes into a standardized alphanumeric designation: the knee abrasion ICD 10 code.
From Diagnosis to Database Entry
The assigned code does not sit in isolation. It becomes part of a comprehensive electronic claim file that typically contains:
- Patient demographic information (name, address, date of birth).
- Insurance policy numbers and billing identifiers.
- Detailed clinical notes and diagnostic codes (like ICD-10 and CPT codes).
- Physician NPI (National Provider Identifier) numbers.
This rich bundle of data is transmitted electronically across local networks, cloud servers, and third-party clearinghouses. Because this information holds immense value on the black market, securing every node of this data pipeline is paramount for healthcare administrators.
Why Diagnostic Codes Matter in Cybersecurity
Cybercriminals do not just target high-profile medical conditions; they target the entire data architecture of healthcare institutions. The connection between routine diagnostic records and cybersecurity lies in data volume and interoperability standards.
The Value of Interoperability and API Security
Modern healthcare systems rely on Application Programming Interfaces (APIs) and interoperability standards like HL7 and FHIR to transmit diagnostic codes and patient records seamlessly between providers, insurers, and public health agencies. Every time a knee abrasion ICD 10 code is queried, transmitted, or updated across an API, a potential entry point for unauthorized access is created.

If an API lacks proper authentication or encryption, attackers can intercept data packets in transit. Consequently, cybersecurity developers must build security frameworks that specifically monitor and protect structured medical data streams, ensuring that even routine transactional data remains confidential and unaltered.
Driving Healthcare Cybersecurity Services Development
The continuous generation of millions of diagnostic codes every day fuels the demand for specialized, healthcare-centric cybersecurity solutions. Standard corporate IT security is often insufficient for clinical environments because healthcare organizations face unique regulatory and operational pressures.
Regulatory Compliance and Protected Health Information (PHI)
Under regulations like the Health Insurance Portability and Accountability Act (HIPAA), any electronic transmission containing diagnostic information tied to a patient's identity constitutes Protected Health Information (PHI). A database leak exposing thousands of records—even if they only detail minor injuries like knee abrasions—triggers mandatory breach notifications, heavy fines, and severe reputational damage.
This regulatory landscape drives healthcare cybersecurity services development toward solutions that offer:
- Granular Access Controls: Ensuring that only authorized billing and clinical personnel can view specific diagnostic and financial records.
- End-to-End Encryption: Protecting data both at rest in EHR databases and in transit across networks.
- Automated Data Loss Prevention (DLP): Monitoring for unauthorized attempts to export bulk medical coding datasets or patient lists.
Securing the Modern Clinical Workflow
Protecting a healthcare network requires a multi-layered defense strategy that accounts for both human error and sophisticated cyber threats like ransomware. Cybersecurity developers must understand clinical realities—such as the need for fast, frictionless data entry by doctors and nurses—when designing security tools.
For instance, if security protocols are too cumbersome, clinicians may resort to insecure workarounds, such as sharing credentials or storing diagnostic notes on unencrypted personal devices. Therefore, modern security development focuses on zero-trust architectures, behavioral analytics, and automated threat detection that operates quietly in the background without disrupting patient care.
Conclusion
The journey of a single diagnostic entry, from a clinician diagnosing a simple scrape to the generation of a knee abrasion ICD 10 code, highlights the intricate relationship between clinical documentation and digital defense. As healthcare continues its digital evolution, the security of everyday medical transactions will remain a top priority. Recognizing how administrative workflows intersect with digital risk underscores the vital need for ongoing innovation in healthcare cybersecurity services development, ensuring that patient data remains secure from intake to archive.