NFC Aouth: Secure Authentication Guide
Near Field Communication (NFC) has transformed how we interact with the physical and digital worlds. From tapping a smartphone at a transit turnstile to paying for groceries with a smartwatch, short-range wireless data exchange is part of daily life. Beneath the convenience of these interactions lies a critical security layer often referred to in developer and security circles as NFC aouth (NFC authentication).

Ensuring that data transmitted over radio waves remains private and tamper-proof is vital. As cyber threats evolve, understanding how authentication protocols protect NFC transactions helps developers build more secure applications and gives users peace of mind.
Understanding NFC Aouth and Core Mechanics
At its core, NFC is a subset of Radio Frequency Identification (RFID) technology operating at 13.56 MHz. It allows two devices—typically an active reader and a passive tag, or two active devices—to communicate when brought within a few centimeters of each other. However, proximity alone does not guarantee security. Eavesdropping and relay attacks remain theoretical risks if proper authentication is missing.
NFC aouth bridges this gap by establishing cryptographic handshakes between the communicating endpoints. Instead of simply broadcasting static identification numbers, modern NFC authentication relies on dynamic tokens, challenge-response mechanisms, and public-key cryptography. This ensures that even if an unauthorized party intercepts the radio signal, the captured data becomes useless for subsequent transactions.
How the Authentication Handshake Works
When an NFC-enabled device approaches a reader, a structured exchange takes place in milliseconds. The primary steps typically include:
- Field Activation: The NFC reader generates an electromagnetic field, powering up the passive tag or waking up the target device.
- UID Exchange: The tag transmits its unique identifier (UID), though this alone is never trusted for high-security operations.
- KChallenge Generation: The reader sends a cryptographic challenge (a random number or nonce) to the target device.
- Signed Response: The target device uses an internal secure element or pre-shared key to sign the challenge and returns the result.
- Verification: The reader or backend server verifies the signature. If valid, access or payment is authorized.
Key Use Cases for NFC Authentication
The applications of secure near-field authentication extend far beyond simple contactless payments. Industries ranging from enterprise security to automotive manufacturing rely heavily on these protocols.
1. Contactless Payment Systems
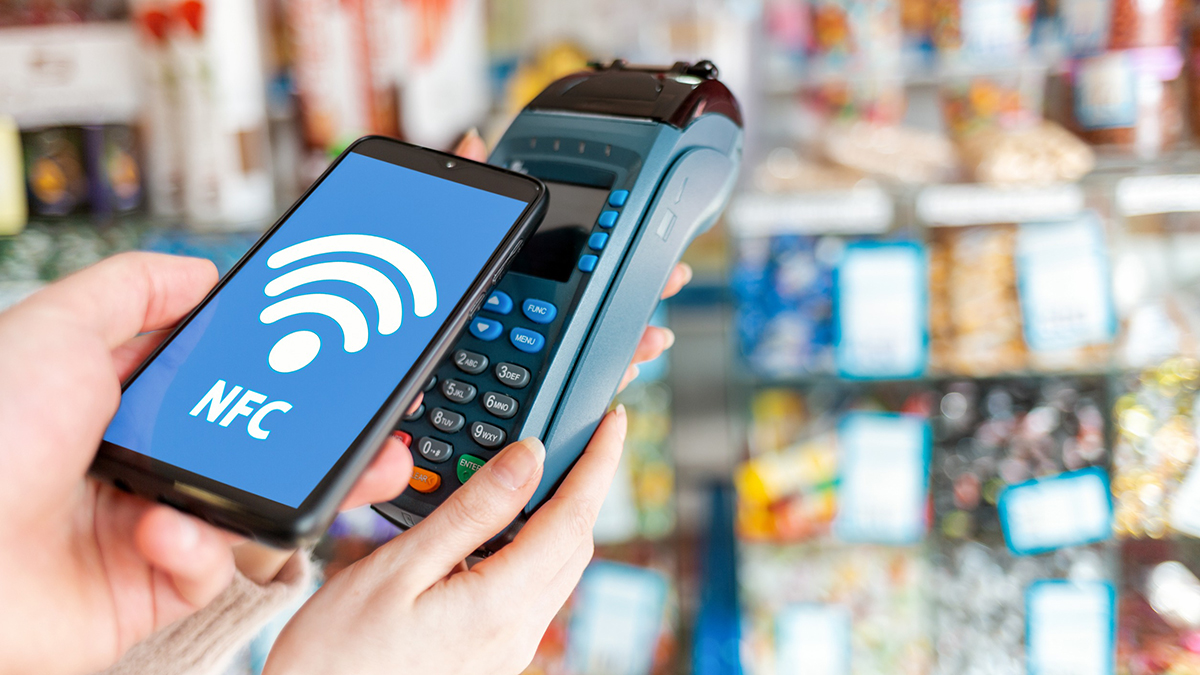
Financial transactions processed via Apple Pay, Google Pay, or contactless credit cards depend on secure tokenization and NFC aouth. Instead of sending actual credit card numbers, the device generates a dynamic, one-time transaction code backed by secure element hardware embedded in the phone.
2. Access Control and Digital IDs

Corporate offices, hotels, and university campuses are rapidly replacing traditional plastic keycards with smartphone-based NFC credentials. Employees can tap their phones against a door reader to unlock office doors. The backend verifies the device's cryptographic identity before releasing the strike lock.
3. Automotive and Digital Keys
Modern vehicles use NFC standards developed by the Car Connectivity Consortium (CCC). Drivers can lock, unlock, and start their vehicles using a smartphone or smart ring. NFC aouth prevents relay attacks that historically plagued traditional key fobs by measuring the precise time-of-flight of the radio signal.
Best Practices for Implementing NFC Security
For software engineers and system architects integrating NFC authentication into new products, following industry standards is crucial. Adopting weak or proprietary encryption schemes often leads to severe vulnerabilities.
- Use Established Standards: Rely on proven standards such as NFC Forum specifications, GlobalPlatform secure element APIs, or ISO/IEC 14443 protocols rather than inventing custom cryptographic flows.
- Leverage Secure Elements (SE): Store sensitive private keys and cryptographic material inside a dedicated hardware Secure Element or Trusted Execution Environment (TEE) rather than standard app storage.
- Implement Mutual Authentication: Ensure that not only does the reader verify the tag, but the tag also verifies the legitimacy of the reader to prevent rogue devices from harvesting sensitive data.
- Keep Firmware Updated: NFC controllers and host operating systems require regular security patches to address newly discovered side-channel attacks and protocol bugs.
Security Challenges and Limitations
While NFC authentication offers robust protection, it is not entirely immune to attack vectors. Understanding these limitations helps engineers design defense-in-depth strategies.
Relay attacks represent a primary concern. In a relay attack, malicious actors use specialized hardware to bridge the physical gap between a victim's card in their pocket and a fraudulent payment terminal far away. Modern protocols mitigate this by measuring transaction latency, making long-distance relays fail due to time-out constraints.
Additionally, physical tampering with low-cost, unprotected NFC tags remains a risk in supply chains and inventory tracking. For critical infrastructure, organizations must deploy encrypted tags with password protection or cryptographic authentication counters.
Conclusion
The reliance on short-range wireless connectivity will only continue to grow as smart cities, IoT devices, and digital wallets expand. Implementing robust NFC aouth protocols ensures that convenience does not come at the expense of security. By combining hardware-level isolation with advanced cryptographic handshakes, developers can deliver seamless, highly secure user experiences across mobile and embedded platforms.