Okta.Catapult: Login, SSO & Setup Guide
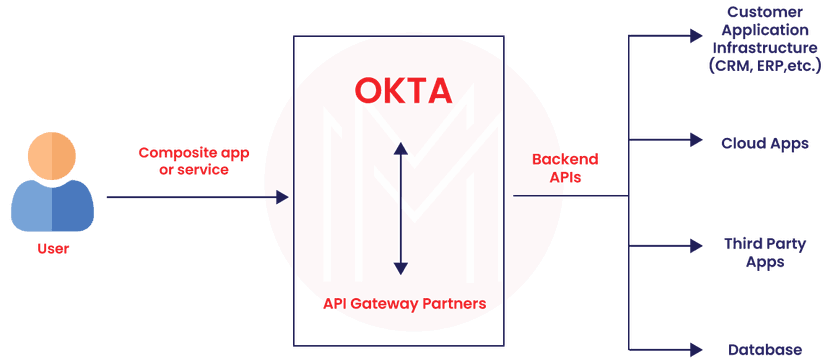
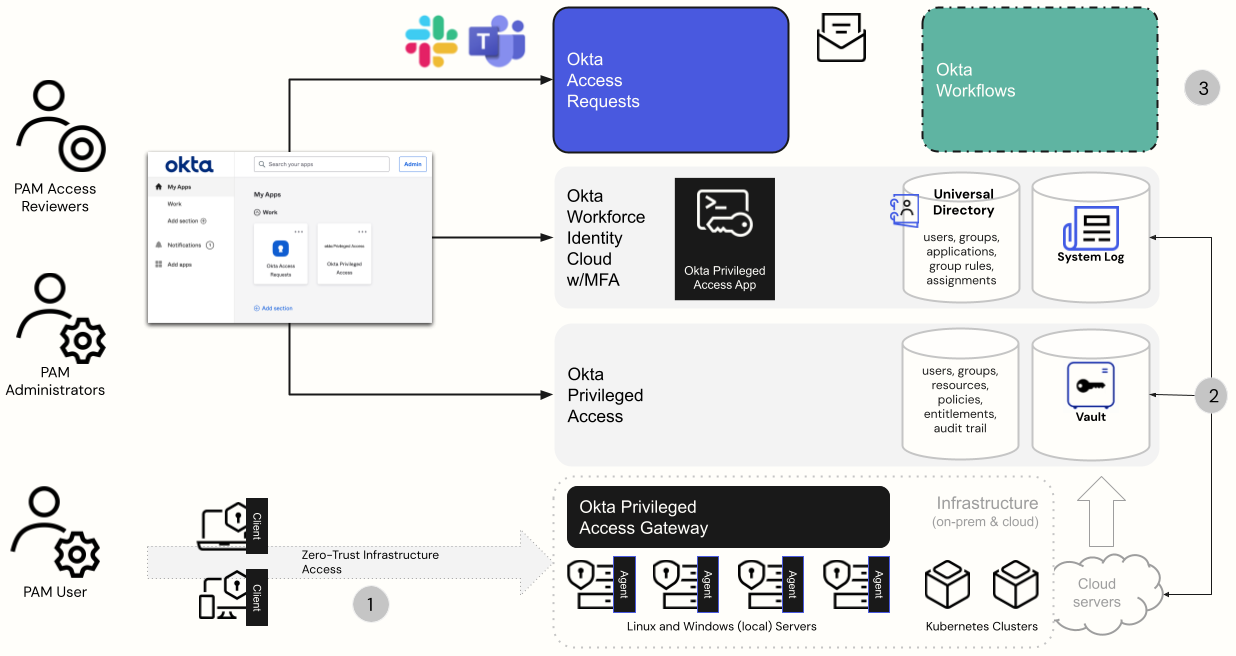
Enterprise security depends on centralized, reliable identity verification, and for thousands of staff members, educators, and enterprise partners, that ecosystem begins at the portal known as okta.catapult. Built on Okta’s enterprise identity cloud, this gateway provides a single entry point to enterprise software, internal communications, human resources records, and proprietary client tools. By centralizing authentication, it eliminates password fatigue while safeguarding sensitive organizational data against credential theft and unauthorized access.

Whether you are an onboarding employee signing in for the first time, a remote worker configuring a new mobile authenticator, or a systems administrator auditing access permissions, understanding how this identity portal operates ensures your workday runs smoothly without compromising company security.
What Is the okta.catapult Portal?
At its core, the portal serves as a custom-configured tenant within the Okta Identity Cloud. Instead of forcing staff to remember dozens of disjointed usernames and complex passwords for platforms like Google Workspace, Microsoft 365, internal analytics, or specialized management suites, the portal employs modern federated identity protocols such as SAML 2.0 (Security Assertion Markup Language) and OIDC (OpenID Connect).
When you authenticate successfully, Okta generates a cryptographically signed digital token that verifies your identity to connected enterprise applications. This delivers three core advantages:
- Frictionless Single Sign-On (SSO): You authenticate once at the start of your shift and gain instant, one-click access to all assigned applications via your personal dashboard.
- Zero Trust Security: The system continuously evaluates contextual risk signals—such as your physical location, device compliance status, and IP reputation—before issuing access tokens.
- Automated Lifecycle Management: When roles change or team members depart, access permissions update across all connected cloud platforms instantaneously, reducing the risk of orphaned accounts.
Step-by-Step: How to Sign In to Your Account
Accessing your daily workstation tools through the portal requires only a standard, supported web browser. Follow these steps to log in:
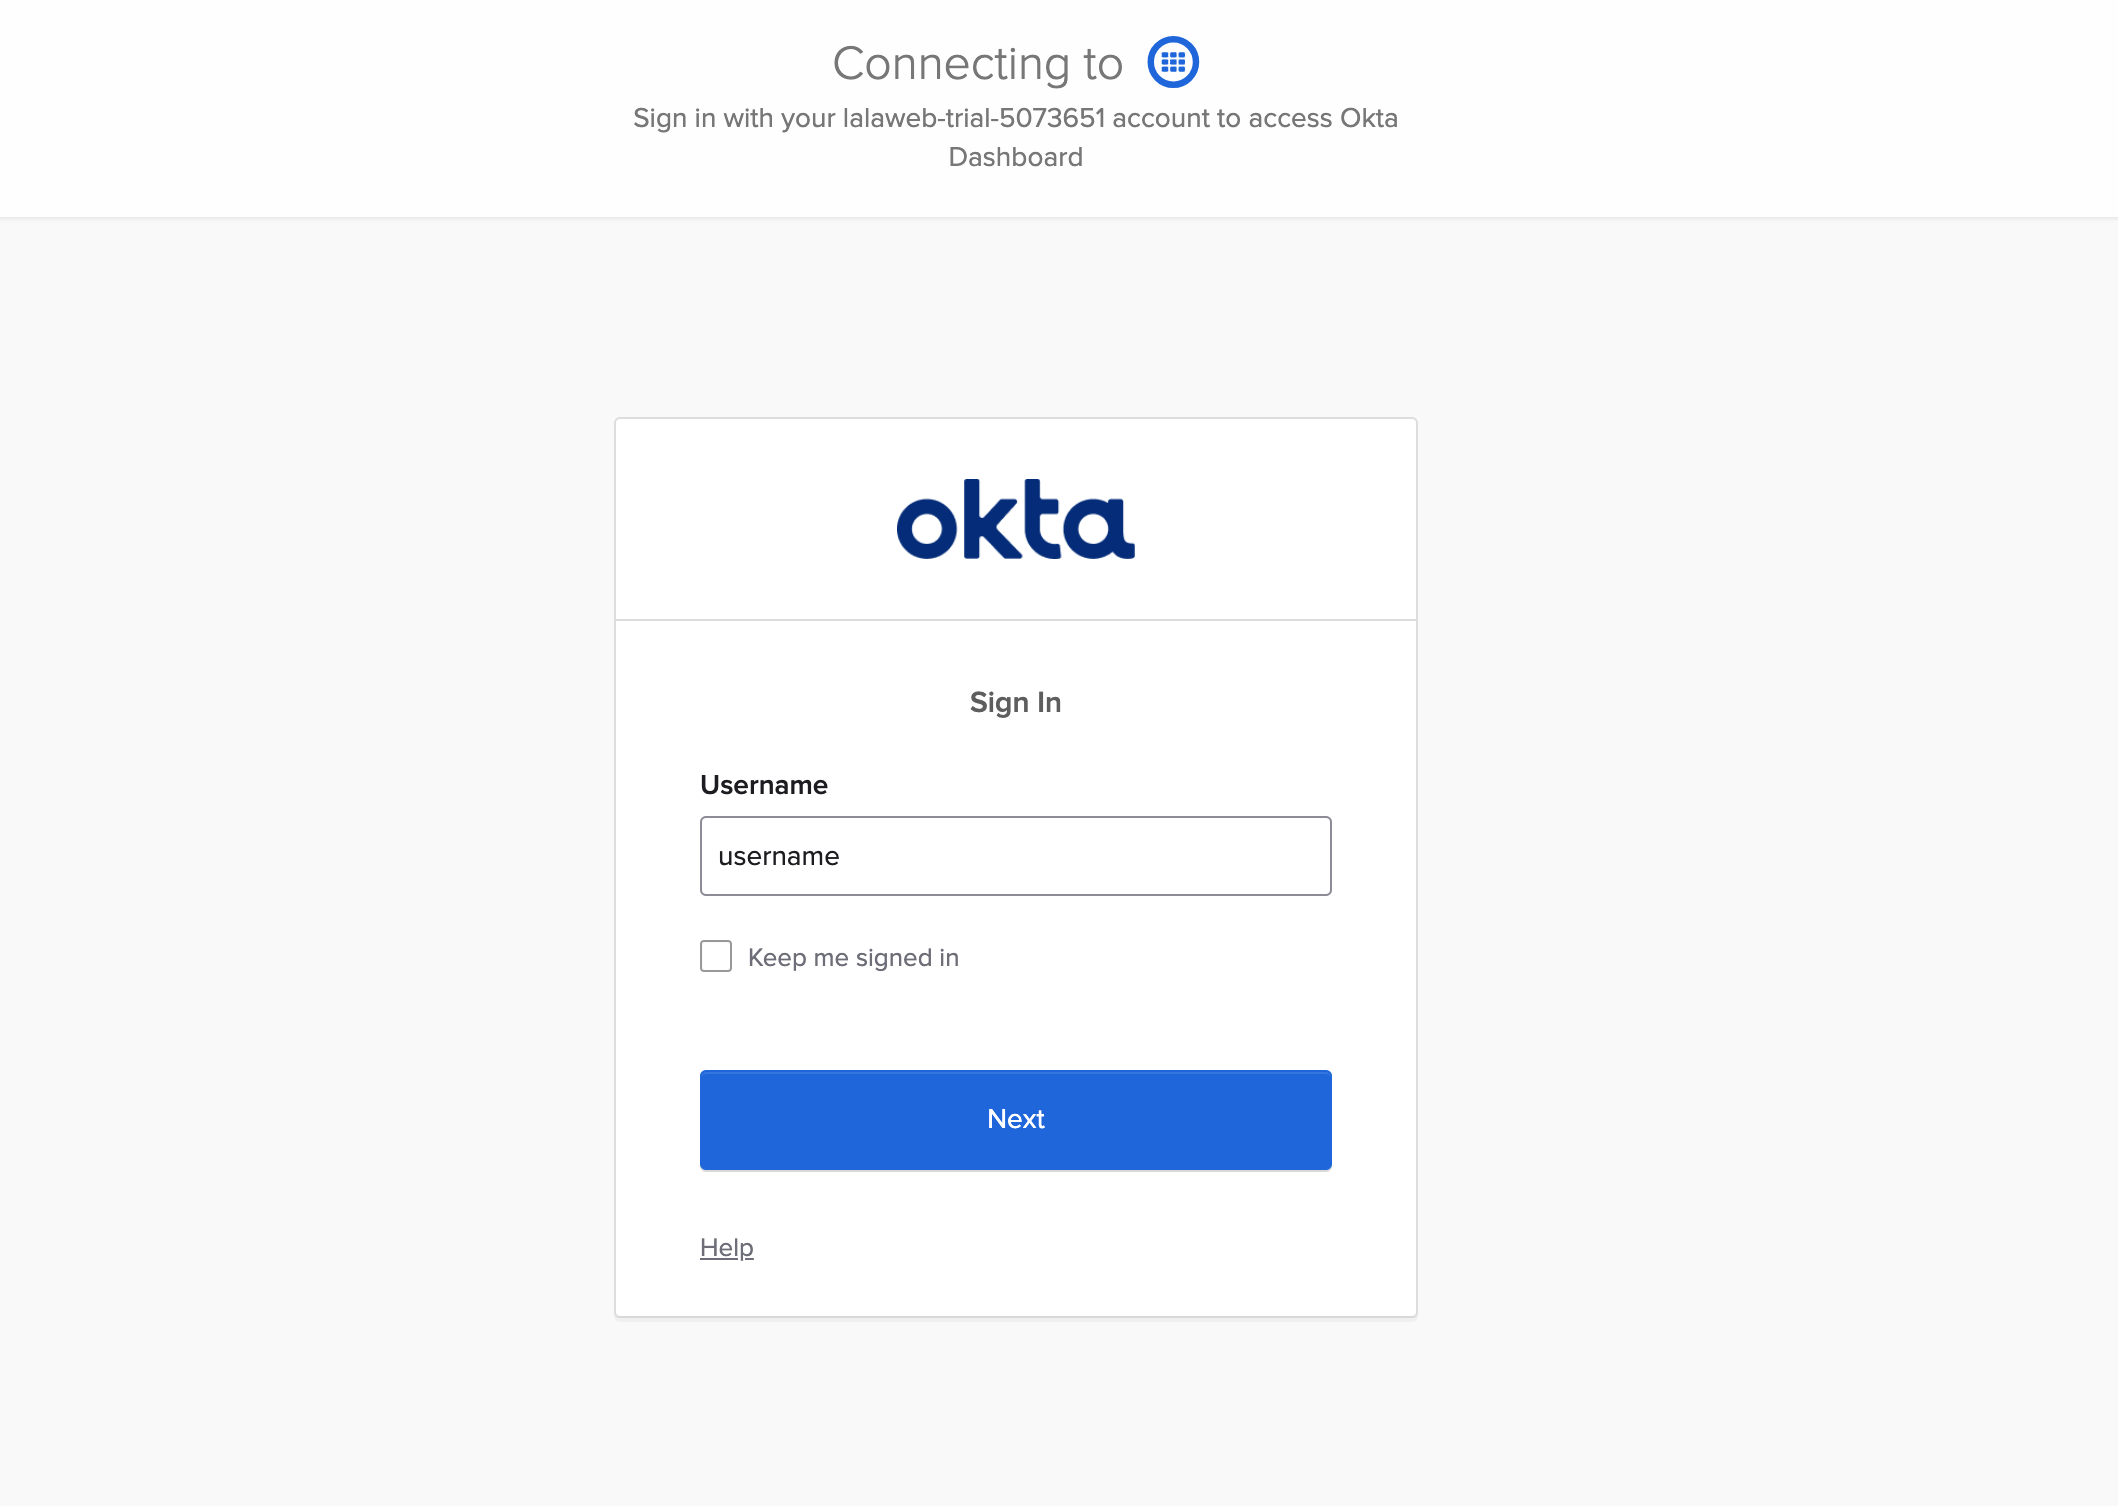
- Navigate to the Official Tenant URL: Open your browser (Google Chrome, Microsoft Edge, Mozilla Firefox, or Apple Safari) and enter your organization’s dedicated Okta URL, typically formatted as
catapult.okta.comor your company’s custom identity subdomain. - Provide Your Username: Enter your full organizational email address or designated employee ID in the username field and click Next.
- Input Your Password: Enter your current password. If this is your first time logging in, use the temporary password provided in your formal onboarding welcome email.
- Complete Multi-Factor Authentication (MFA): When prompted, verify your identity using your assigned secondary authentication factor, such as a push notification on your smartphone or a one-time passcode.
- Access Your Dashboard: Once verified, you land on your personalized dashboard displaying launch icons for every internal system and third-party service assigned to your role.
Setting Up Multi-Factor Authentication (MFA)
Multi-Factor Authentication is an essential requirement on modern identity platforms. Even if malicious actors intercept your password through phishing or credential stuffing, MFA prevents them from breaching the perimeter without physical access to your secondary verification device.
Configuring Okta Verify
Okta Verify is the recommended authenticator application for mobile devices (iOS and Android). To configure it:
- Download the Okta Verify app from the official Apple App Store or Google Play Store.
- On your computer screen, select Okta Verify as your authentication method during initial portal setup. The screen will generate a unique QR code.
- Launch the app on your mobile device, tap Add Account, select Organization, and point your camera at the QR code displayed on your monitor.
- Once paired, enable biometric authentication (Face ID, Touch ID, or fingerprint scanning) within the app to ensure your phone cannot be used by unauthorized individuals.
Alternative Verification Factors
Depending on organizational policy, administrators may permit secondary or backup factors:
- FIDO2 / WebAuthn Hardware Keys: Physical USB keys (such as YubiKeys) that deliver phishing-resistant authentication through hardware cryptographic checks.
- Third-Party Authenticator Apps: Generic TOTP (Time-based One-Time Password) apps like Google Authenticator or Microsoft Authenticator.
- SMS or Voice Codes: A short numeric code sent to a verified mobile phone number. While convenient, this method is generally discouraged for high-privilege accounts due to SIM-swapping risks.
Troubleshooting Common okta.catapult Issues
Authentication problems can halt productivity. Below are the most common technical hitches encountered on the portal along with straightforward steps to resolve them.
1. Account Lockouts and Expired Passwords
Repeated failed login attempts trigger an automated lockout policy to neutralize brute-force attacks. If your account locks:
- Wait 15 to 30 minutes for the automated lockout counter to reset, provided your organization enables self-service unlock.
- Click the Need help signing in? link directly beneath the login fields and select Reset Password or Unlock Account. Follow the verification prompts sent to your recovery email or phone.
- If your profile does not support self-service recovery, contact your internal IT helpdesk to have an administrator clear the lockout status and issue a temporary bypass code.
2. MFA Desynchronization or New Mobile Devices
Upgrading to a new phone often breaks the connection with Okta Verify if the old device is wiped before migrating the profile. If you are stuck at the MFA prompt:
- Click Verify with something else on the prompt screen to see if you have an alternative factor registered, such as an SMS code or a secondary tablet.
- If no secondary factor exists, reach out to your IT administrator. They must reset your MFA profile from the Okta Admin Console, which triggers a fresh enrollment wizard during your next login.
3. Application Missing from the Dashboard
If an application you need for daily operations is not visible on your home screen:
- Use the search bar at the top of the dashboard to ensure the icon is not simply hidden inside a collapsed category.
- Confirm your current role assignments with your department manager. Okta provisions software based on security groups; if your account was not added to the relevant group, the corresponding tile will not appear.
- Refresh your session by logging out and signing back in to pull the newest entitlement catalog.
4. Browser Redirect Loops and Stale Cookies
Occasionally, signing into the portal results in an endless loading loop or an HTTP 400 Bad Request error. This occurs when corrupted session cookies conflict with active SAML assertions:
- Clear your browser’s cache and cookies for the past 24 hours.
- Attempt the login process using a private or incognito browsing window. If this works immediately, an installed browser extension or cached cookie is the culprit.
- Ensure your operating system’s clock is synchronized automatically via network time servers; clock skews exceeding five minutes can invalidate cryptographic security tokens.
Security Best Practices for End Users
While enterprise identity systems provide robust perimeter defenses, individual user habits remain the primary vector targeted by cyber threats. Follow these golden rules whenever working inside your account:
- Check the Address Bar: Always confirm that the domain in your browser matches the verified URL before typing your credentials. Beware of typosquatting domains designed to mimic your company’s login page.
- Never Approve Unprompted Push Notifications: If your phone receives an Okta Verify push notification when you are not actively logging in, tap Deny immediately and report the incident to your security operations team. This is a telltale sign of an MFA fatigue attack.
- Log Out of Shared Terminals: If you use a shared or loaner workstation, always click your name in the upper right corner, select Sign Out, and close all browser windows completely before stepping away.
Summary
The okta.catapult environment is designed to streamline your daily workflow while providing defense-in-depth protection for organizational infrastructure. By registering dependable multi-factor devices, practicing good browser hygiene, and recognizing standard troubleshooting pathways, you can maintain seamless, uninterrupted access to all your critical work applications.