Peachjar Leaks Explained: Inside The Warnings
When school districts transition from paper backpack flyers to digital distribution platforms, convenience usually takes center stage. Peachjar is one of the most widely adopted digital flyer management systems in the United States, connecting PTAs, community organizations, and schools directly with parents via email. However, digital platforms handling student and family information naturally attract scrutiny. Rumors, alerts, and discussions surrounding Peachjar leaks explained have left many parents and administrators wondering about the true safety of their data.
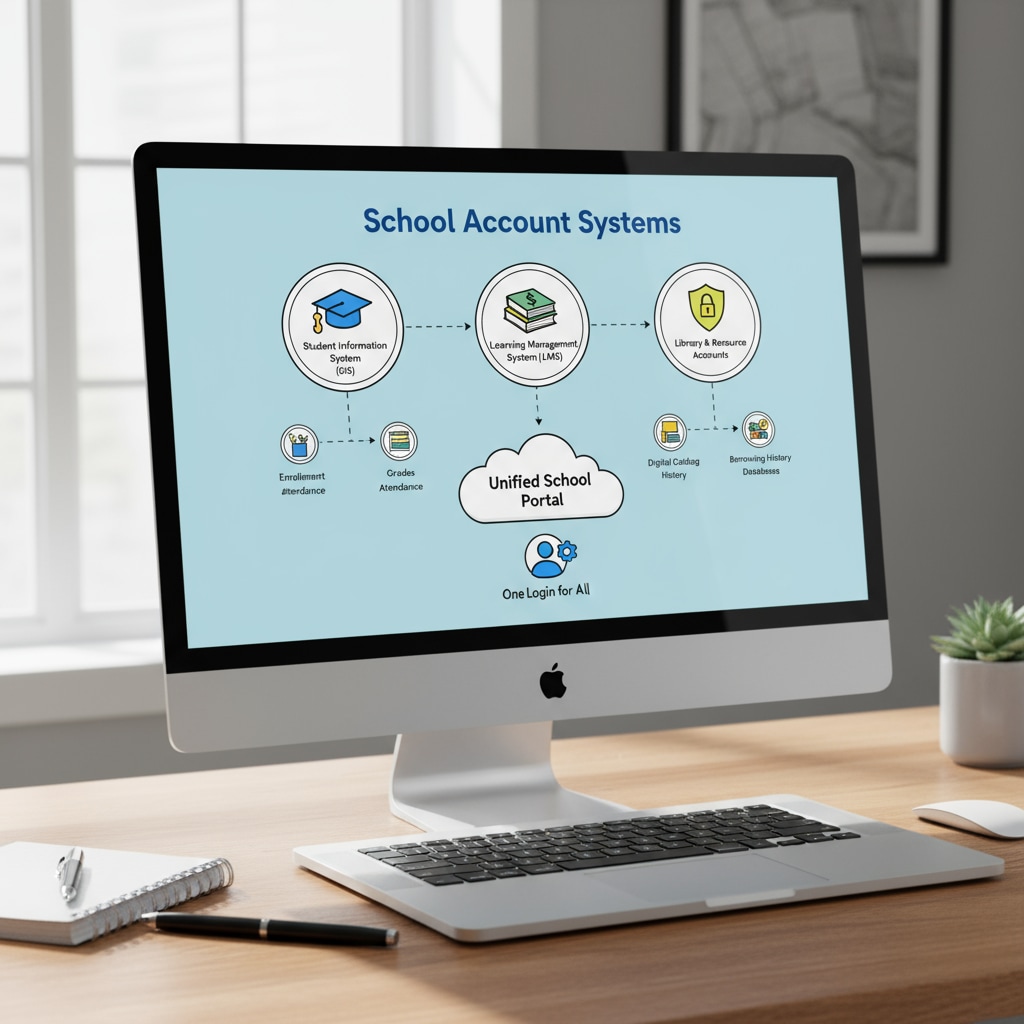
Understanding what these warnings actually entail requires separating platform-wide data breaches from third-party advertising risks, misconfigured settings, and broader concerns about digital school ecosystems. This guide breaks down the security architecture of Peachjar, analyzes past warnings, and provides actionable steps for families to protect their information.
What Is Peachjar and How Does It Handle Data?
Before examining potential vulnerabilities, it helps to understand how the platform operates. Peachjar acts as an intermediary between school districts and approved community partners (such as youth sports leagues, tutoring centers, and local theaters). Instead of stuffing backpacks with paper flyers, districts upload parent email lists or integrate with student information systems (SIS) to route digital flyers straight to inboxes.
Because the platform interacts directly with school district databases, security is paramount. Peachjar utilizes encryption protocols for data in transit and at rest, and access is typically restricted to authorized district personnel and approved vendor administrators. However, the sheer volume of PII (Personally Identifiable Information)—including parent names, student grade levels, and email addresses—makes any educational technology platform a high-profile target for cybersecurity concerns.
Peachjar Leaks Explained: Unpacking the Security Warnings
When headlines or social media posts mention security warnings regarding school communication tools, it usually stems from one of a few distinct scenarios. To fully understand Peachjar leaks explained, we must categorize these warnings into distinct types.
1. Third-Party Vendor and Partner Phishing Risks
One of the most common threats associated with digital flyer platforms isn't a direct database breach of Peachjar's core servers, but rather the vetting process of third-party organizations. Because hundreds of local businesses and community organizations apply to send flyers through the system, bad actors occasionally attempt to slip past verification checks.
Security researchers have warned that if a malicious entity manages to gain approval as a community partner, they could theoretically design flyers containing deceptive links—effectively turning the platform into a conduit for phishing campaigns. While Peachjar employs manual and automated screening processes to catch these attempts, vigilance from parents remains critical.
Video: Peachjar Overview
.png#keepProtocol)
2. Data Broker Integration and Privacy Concerns
Another major driver of warnings involves data privacy policies rather than traditional hacker breaches. Parents frequently express concern over how email lists are synced and whether user behavior tracking is shared with advertisers.
Like many free or low-cost SaaS tools for schools, monetization relies heavily on sponsored content and targeted community advertising. While this does not constitute a data "leak" in the traditional sense of stolen credentials, privacy advocates often raise red flags regarding how extensively user engagement data is monitored and whether school districts adequately inform parents about data-sharing agreements under FERPA and COPPA guidelines.
3. Misconfigured District Accounts and Human Error
In the vast majority of EdTech security incidents across the United States, the root cause is human error rather than sophisticated cyberattacks. Local school administrators occasionally misconfigure permission settings, export contact lists to insecure local drives, or use weak, shared passwords for their administrative dashboards.
When a district experiences an isolated security incident involving its communication channels, the blame is often misattributed entirely to the platform itself, generating widespread panic among parent communities.
How to Protect Your Family's Data
While school districts choose and manage these software integrations, parents can take proactive measures to minimize digital exposure:
- Use a Dedicated Family Email: Consider setting up an email address specifically for school communications, separate from your primary work or personal financial accounts.
- Scrutinize Flyer Links: Never click on direct links inside a digital flyer if the destination URL looks suspicious or requests sensitive login credentials. Navigate to the organization's official website independently.
- Review District Privacy Policies: Check your school district’s annual notice regarding directory information and third-party software tools to understand your opt-out rights.
- Unsubscribe When Necessary: If you no longer wish to receive updates from specific community groups or find the digital flyer volume overwhelming, use the official opt-out links provided at the bottom of the emails.
The Bottom Line on EdTech Security
Digital flyer distribution has made school-to-home communication vastly more efficient, but it requires a careful balance between convenience and cybersecurity. When looking at Peachjar leaks explained, the reality is a mix of standard digital hygiene practices, vigilant third-party monitoring, and robust district-level administration. By staying informed about how your school district manages its software vendors, you can safely navigate digital platforms without compromising your family's privacy.


.png?width=1000&height=750&name=Peachjar %26 Peachjar %2B AiDA Comparison Chart (3).png)