Secure Your TIAA CREF Login and Protect Your Future
Your retirement account represents decades of hard work, discipline, and long-term planning. Because institutional retirement plans hold substantial sums of capital, accounts held with the Teachers Insurance and Annuity Association of America (TIAA, formerly TIAA-CREF) have increasingly become attractive targets for sophisticated cybercriminals. If you want to protect your future, secure your TIAA CREF login my account access immediately to ensure your savings remain out of reach from identity thieves and unauthorized third parties.
Whether you work in higher education, healthcare, research, or the non-profit sector, maintaining strict digital hygiene around your retirement portal is no longer optional. This guide outlines the exact steps required to navigate the official login portal safely, deploy advanced account protections, and monitor your portfolio against emerging cyber threats.
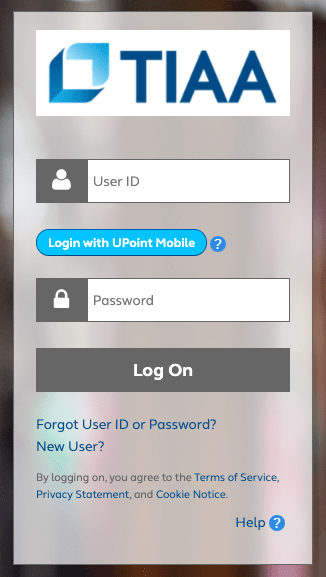
How to Safely Navigate the TIAA Login Portal
Cybercriminals frequently use credential harvesting schemes—such as lookalike websites and search engine ad spoofing—to intercept user credentials. Before you enter your username or password, verify that you are connecting through the official channel.
- Direct Navigation: Always type
https://www.tiaa.orgdirectly into your browser's address bar rather than clicking links inside emails or clicking sponsored search engine ads. - Check the SSL/TLS Certificate: Ensure the padlock icon is visible in your browser's address bar, indicating an encrypted, authentic connection to TIAA.
- Avoid Shared Devices: Never log in to your financial portals using public computers at libraries, hotels, or unsecured public Wi-Fi networks where keyloggers or packet-sniffing software might be active.
Why You Must Secure Your TIAA CREF Login My Account Now
Retirement accounts differ fundamentally from checking accounts. Because investors review their 401(k), 403(b), or IRA balances only once a quarter or once a year, unauthorized activity can go unnoticed for months. Implementing proactive defenses drastically reduces the window of opportunity for bad actors.
1. Activate Enhanced Multi-Factor Authentication (MFA)
Standard password protection is no longer sufficient on its own. Multi-factor authentication requires a second layer of verification before granting access to your account balances, loan options, and withdrawal forms.
Log in to your TIAA account, navigate to the Security Settings section, and enable two-step verification. Where possible, choose an authenticator app (such as Google Authenticator, Microsoft Authenticator, or an enterprise token) or TIAA's proprietary verification prompts rather than SMS text messaging, which can be vulnerable to SIM-swapping exploits.
2. Create a Robust, Unique Passphrase
Password reuse is one of the leading causes of account takeover. If a data breach occurs at an unrelated retail site where you used the same password, attackers will automate credential-stuffing attacks against major financial institutions like TIAA.
- Use a passphrase of at least 16 to 20 characters composed of unrelated words, numbers, and symbols.
- Avoid personal identifiers such as your birth year, your institution's name, or common retirement terms.
- Store your complex credentials inside an encrypted password manager rather than browser autofill or desktop sticky notes.
3. Turn On Real-Time Alerts and Notifications
TIAA offers account alerts via email and SMS text. Activating these alerts ensures you receive real-time notifications whenever high-risk actions occur on your profile. Ensure notifications are triggered for:
- Profile updates (changes to your residential address, email, or telephone number).
- Password resets or multi-factor authentication changes.
- Withdrawal, rollover, or loan requests.
- New linked bank accounts or modifications to direct deposit routing details.
Recognizing Phishing Attacks Aimed at TIAA Members

Social engineering remains the primary vector for unauthorized account breaches. Scammers frequently masquerade as TIAA representatives, sending urgent emails claiming your account is locked, your portfolio requires re-verification, or your pension payment has failed.
To avoid falling victim to these schemes, remember these core rules:
- TIAA will never call or text asking for your one-time passcode. If an inbound caller claims to be from TIAA fraud prevention and requests a numeric code sent to your phone, hang up immediately.
- Inspect sender domains carefully. Legitimate communications originate from authentic domains (such as
@tiaa.org). Be wary of subdomains or altered spellings. - Never verify credentials via email links. If an email warns you of a problem, open a clean browser tab, go to the official portal independently, and check the internal message center.
Post-Login Security Checklist: Audit Your Account Today
Once you are safely inside the portal, conduct a brief audit to ensure your records reflect your intended configurations.
Review Beneficiary Designations
Beneficiary designations override instructions written into wills. Periodically check that your primary and contingent beneficiaries are up to date, their Social Security numbers are accurate, and no unauthorized entities have been appended to your funds.
Confirm Linked Financial Institutions
Examine the external banking institutions registered under your transfer settings. If you notice any unfamiliar bank routing or account numbers, alert TIAA fraud specialists immediately, as this is often the preparatory step an intruder takes before initiating a fraudulent distribution.
Inspect Connected Third-Party Aggregators
Many individuals link their TIAA accounts to third-party budgeting software or net-worth tracking applications. Review and revoke access tokens for old or unused financial management apps that may retain historical data or API access to your profile.
What to Do If You Detect Suspicious Activity
If you observe unauthorized profile modifications, receive a verification code you did not initiate, or see unexpected transactions on your statements, take fast, decisive action:
- Contact TIAA Directly: Call TIAA's official customer service line (1-800-842-2252) and request the Fraud and Identity Theft department. Ask them to place an immediate administrative freeze on distributions and profile alterations.
- Reset Your Credentials: Change your password immediately from a secure, clean device. Terminate all active web sessions across other devices if prompted.
- Notify Your Employer's HR/Benefits Administrator: If your account is tied to an employer-sponsored 403(b) or 401(a) plan, inform your institutional benefits office so their compliance team can monitor institutional feeds.
- Place a Credit Freeze: Contact the three major credit bureaus (Equifax, Experian, and TransUnion) to freeze your credit files, preventing bad actors from opening lines of credit with stolen personally identifiable information (PII).
Your retirement assets represent a lifetime of commitment. Taking fifteen minutes today to establish strict login safeguards, review account permissions, and deploy multi-factor authentication provides indispensable protection for your financial future.