The Truth Inside: How the MistyRay Breach Rushed Cybersecurity Overhaul
Introduction

In the digital age, cybersecurity incidents occur with alarming frequency. Yet, rare is the event that fundamentally shifts industry standards overnight. The MistyRay breach stands out as one of those watershed moments. When unauthorized actors penetrated MistyRay’s supposedly bulletproof architecture, it sent shockwaves through the tech ecosystem. The Truth Inside: How the MistyRay Breach Rushed Cybersecurity Overhaul reveals the gritty reality of what happened behind closed doors, exposing systemic vulnerabilities and sparking a frantic race to re-engineer modern digital defense.
For years, organizations relied on perimeter-based security models, assuming that keeping bad actors outside the fence was enough. The MistyRay incident shattered that illusion, proving that sophisticated attackers could not only bypass standard defenses but also dwell undetected for months. This deep dive explores the anatomy of the breach, its immediate fallout, and the lasting changes it forced upon the cybersecurity landscape.
Anatomy of a Catastrophe
To understand why the MistyRay breach triggered such an aggressive industry-wide reaction, we must look at how the attack unfolded. Unlike typical ransomware hits that announce themselves immediately with a glowing red decryption screen, the MistyRay incident was a textbook Advanced Persistent Threat (APT).
The Initial Vector and Dwell Time
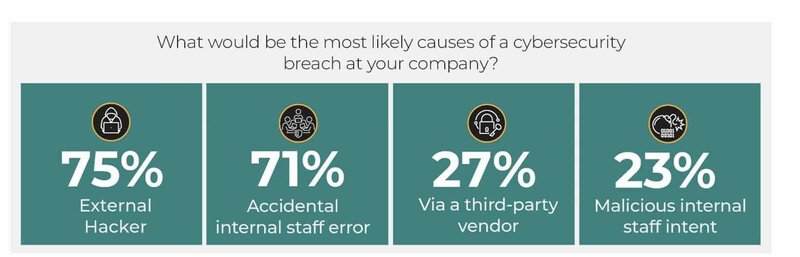
Attackers did not break in through a dramatic zero-day exploit in the core database. Instead, they utilized a compromised vendor credential—a classic supply chain vulnerability. By exploiting third-party access rights, the threat actors slipped into the network quietly. Once inside, they spent over 180 days mapping internal systems, escalating privileges, and harvesting sensitive intellectual property and customer data without triggering traditional alert thresholds.
The Scale of Exposure
When the breach was finally discovered, the numbers were staggering. Millions of user records, proprietary source code, and internal communications were exfiltrated. The sheer depth of the access shocked security analysts. It became painfully clear that once the perimeter defense failed, the internal network was essentially an open highway.
The Catalyst for Change: Why the Incident Forced Immediate Action
Security breaches happen every day, so why did MistyRay become the catalyst for a massive cybersecurity overhaul? The answer lies in the company's profile, the sensitivity of the data involved, and the glaring incompetence exposed in their incident response plan.
Video: Australia's National Cybersecurity Overhaul As Fears Of Data Breaches Grow | 10 News First

- Regulatory Pressure: The sheer volume of exposed consumer data caught the attention of global regulators, leading to record-breaking fines and intense scrutiny.
- Boardroom Panic: For the first time, corporate boards realized that a cybersecurity failure was not just an IT problem—it was an existential business threat that could wipe out market capitalization in days.
- Vendor Ecosystem Vulnerability: It proved that securing your own house is useless if your supply chain partners leave their front doors wide open.
The Blueprint of the Modern Cybersecurity Overhaul
In the wake of the MistyRay disaster, organizations across the globe abandoned complacency. Budgets were rewritten, security chiefs were given direct access to executive boards, and a total architectural rethink began. Several core principles defined this new era of defense.
Adopting Zero Trust Architecture
The old mantra of "trust but verify" was officially retired. Organizations rapidly transitioned to Zero Trust Architecture (ZTA), which operates on the principle of "never trust, always verify." Under this model, every user, device, and application attempting to access internal resources must be continuously authenticated and authorized, regardless of whether they are sitting inside the corporate office or logging in from home.
Advanced Endpoint Detection and Response (EDR)
Traditional antivirus software relies on signature-based detection, making it useless against novel attacks. The MistyRay breach forced companies to deploy advanced EDR and Extended Detection and Response (XDR) tools. These systems use behavioral analytics and machine learning to spot anomalies in real-time, catching lateral movement before damage can be done.
Rigorous Third-Party Risk Management
Recognizing that the initial vector was a third-party vendor, companies implemented strict vendor risk management frameworks. Continuous monitoring of supply chain partners, mandatory multi-factor authentication (MFA) for all external integrations, and regular security posture assessments became non-negotiable requirements for doing business.
Lessons Learned for the Future
The MistyRay breach was a painful and expensive lesson, but it ultimately made the digital ecosystem more resilient. It stripped away the illusion of security that many enterprises had grown comfortable with. By exposing the fatal flaws in perimeter defenses, it accelerated the adoption of technologies and philosophies that should have been standard years prior.
Today, the legacy of the MistyRay incident serves as both a warning and a benchmark. As cyber threats continue to evolve with the advent of generative AI and automated hacking tools, the lessons learned from that fateful breach remind us that cybersecurity is not a destination, but a continuous, unyielding process of adaptation.