Time to Act: What the MythicLeak Means for Your Security
In the fast-paced world of digital data, new vulnerabilities emerge almost daily, but few events capture public and industry attention quite like a major unauthorized data exposure. Recently, security analysts and IT professionals have been buzzing about a significant incident dubbed the MythicLeak. For everyday internet users and business owners alike, headlines about massive data drops can feel abstract until they hit close to home. However, waiting for confirmation that your specific data has been compromised is a dangerous strategy. It is truly Time to Act: What the MythicLeak Means for Your Online Security dictates that we look past the sensational headlines and focus on practical, hardened defenses.

Understanding the scale and nature of this leak helps demystify the threat and provides a clear roadmap for what needs to be done. Whether you manage a corporate network or simply want to protect your personal email and banking logins, this incident serves as an urgent reminder of how fragile our digital perimeter can be.
Decoding the Incident: What Is the MythicLeak?
Every major data exposure has unique characteristics that dictate how dangerous it is to the general public. While specific details surrounding the origin of the MythicLeak continue to evolve as forensic investigators analyze the compromised datasets, the core pattern mirrors many historical breaches: a massive repository of sensitive information has found its way into unauthorized hands.
Typically, these leaks involve combinations of user credentials, personal identifiable information (PII), and internal configuration details. When bad actors gain access to such extensive troves, they rarely use the data manually. Instead, they deploy automated tools to test these credentials across thousands of popular websites and financial services in a process known as credential stuffing.
Why This Leak Is Different
Security experts analyze every breach to determine its severity score. The MythicLeak stands out due to the sheer diversity of the exposed records. It is not limited to a single platform or a specific demographic. Instead, it spans multiple digital ecosystems, meaning that users who practice poor password hygiene—such as reusing the same password across multiple platforms—are at an exceptionally high risk of secondary compromises.
Immediate Steps: Time to Act: What the MythicLeak Means for Your Online Security
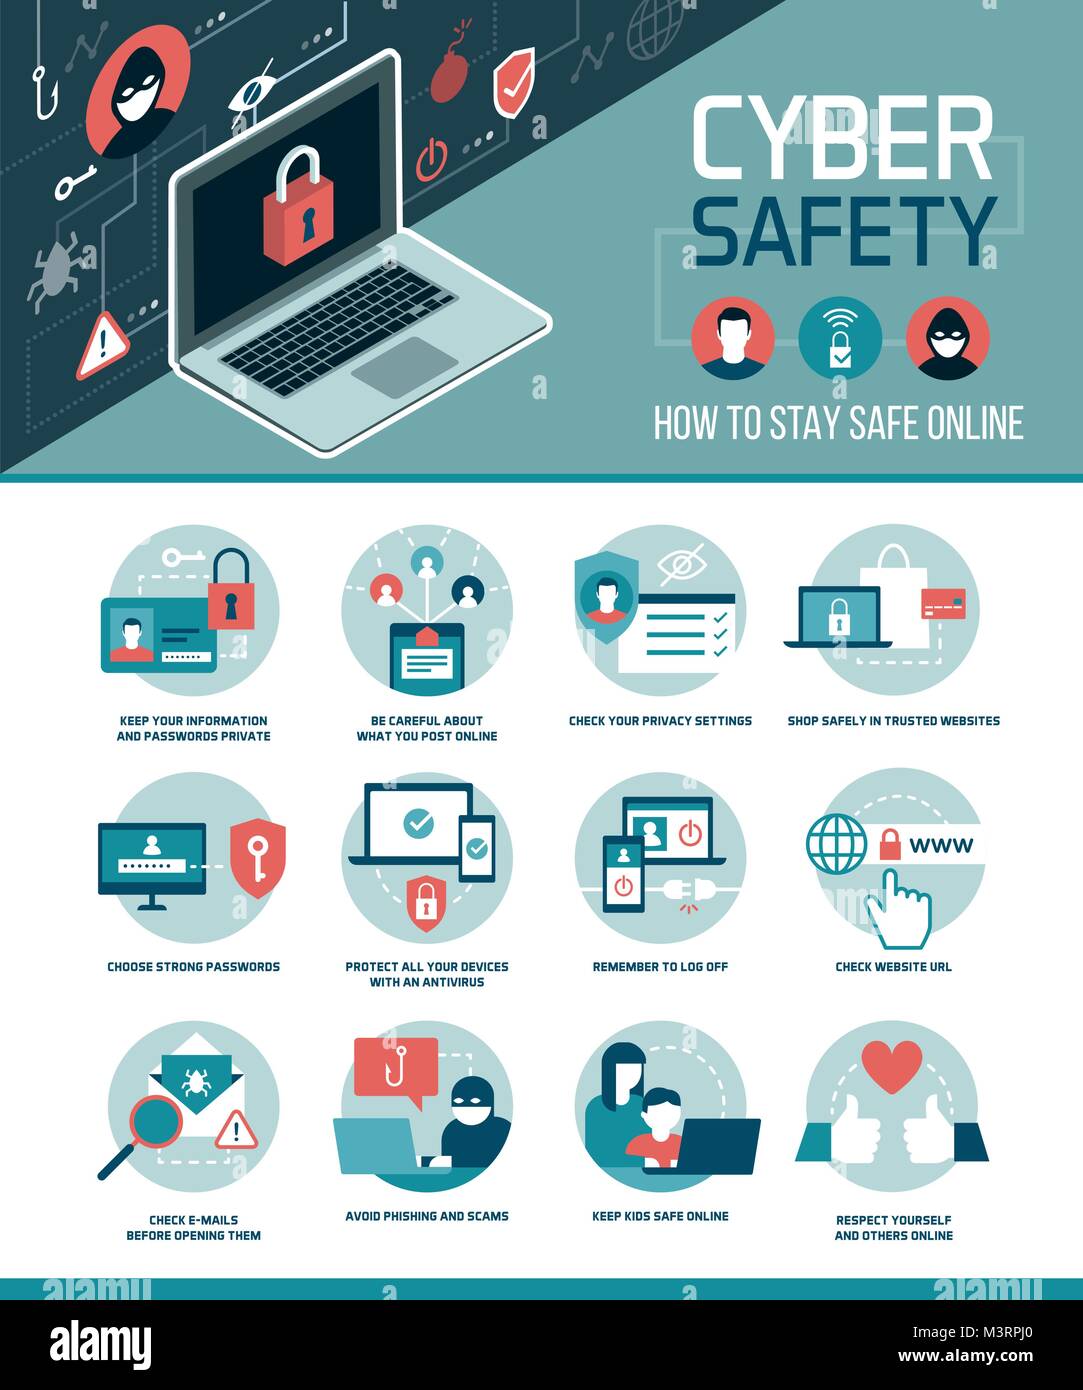
Panicking will not secure your accounts, but decisive action will. If you want to insulate yourself from the fallout of this incident, you need to execute a methodical cleanup of your digital life. Here is a prioritized checklist to help you lock down your accounts today.
- Check Your Exposure Status: Utilize reputable breach-notification platforms (such as Have I Been Pwned) to see if your primary email addresses appear in known data dumps associated with recent incidents.
- Overhaul Your Passwords: Stop reusing passwords immediately. If an exposed credential matches a login you use for banking, social media, or work, change it at once.
- Implement Multi-Factor Authentication (MFA): Even if a bad actor manages to acquire your password through a leak like MythicLeak, robust MFA acts as a brick wall. Enable app-based authenticators or hardware security keys wherever possible.
- Monitor Your Financial Accounts: Keep a close eye on credit card statements and bank alerts for any unusual or unauthorized micro-transactions.
Long-Term Defensive Strategies for the Post-MythicLeak Era
Video: What Mythos Means - Marketing or Mayhem

Once you have addressed the immediate vulnerabilities, you must shift your mindset from reactive defense to proactive hardening. Incidents like the MythicLeak prove that perimeter security alone is no longer enough. Zero-trust principles and modern identity management tools must become the standard for both individuals and organizations.
Adopt a Password Manager
Human memory is simply not equipped to handle the dozens of complex, unique passwords required in the modern digital age. Investing in a reputable, encrypted password manager eliminates the temptation to reuse weak passwords. These tools generate random, highly secure login credentials for every site you visit and autofill them securely.
Audit Your Digital Footprint
Over the years, most of us accumulate dozens of unused online accounts tied to old email addresses. Each forgotten account is an unmonitored vulnerability. Take an afternoon to permanently delete accounts you no longer use, effectively reducing your attack surface and limiting the damage potential of future data exposures.
What Businesses Must Learn from the Incident
If you are a business owner or IT administrator, the MythicLeak carries organizational implications that go far beyond individual password resets. Supply chain vulnerabilities and employee credential hygiene remain the weakest links in corporate security architectures.
- Deregulate shadow IT by strictly auditing which third-party software and SaaS applications your team connects to company networks.
- Conduct mandatory security awareness training to help employees spot sophisticated phishing attempts that often follow major public data leaks.
- Enforce enterprise-grade identity and access management (IAM) solutions with conditional access policies.
Conclusion: Turning Awareness into Action
Security incidents can feel overwhelming, but they also provide a valuable catalyst for positive change. The discussions surrounding the MythicLeak should not induce fear, but rather motivate us to upgrade our digital hygiene. By updating vulnerable credentials, adopting modern password management tools, and implementing multi-factor authentication across all critical platforms, you render incidents like this powerless against your personal data. The digital landscape will always present new threats, but staying proactive is your best defense.