WakeMed Remote Access Guide: Is It Worth the Risk?
In modern healthcare, the ability to view patient charts, check schedules, and handle administrative duties off-site is more than a luxury—it is a necessity. For healthcare professionals and staff affiliated with WakeMed Health & Hospitals, connecting from home or a mobile device keeps operations running smoothly. However, opening network pathways beyond the hospital's physical walls introduces complex security challenges. This WakeMed remote access guide: Is it REALLY worth the risk? examines how the system operates, the safeguards in place, and whether logging in from outside the facility is a safe bet.

Understanding WakeMed Remote Access
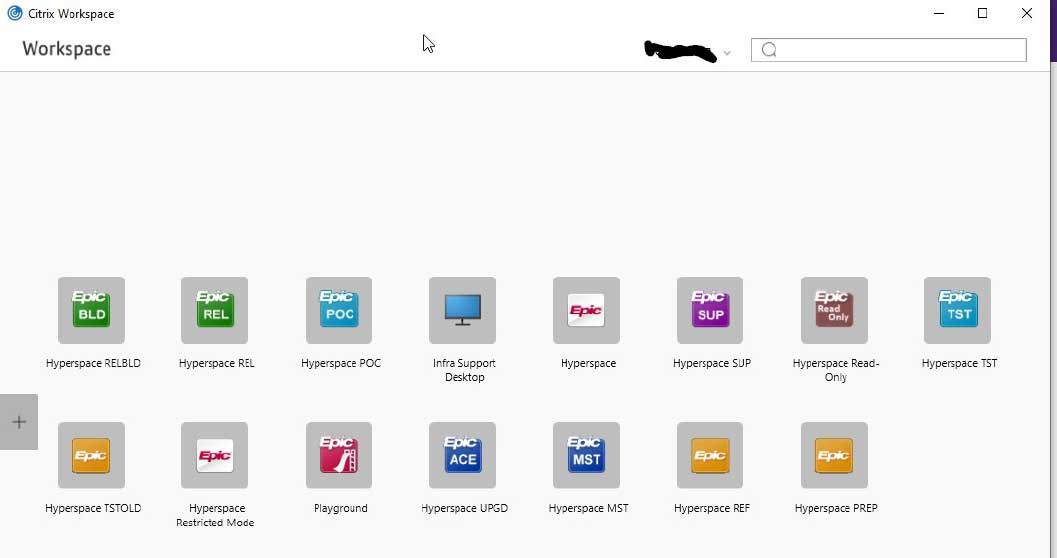
WakeMed utilizes specialized portal infrastructure and Virtual Private Network (VPN) technology to allow authorized personnel to connect to internal resources. Whether you are a physician reviewing lab results, a nurse checking shift swaps, or an administrative worker handling billing, these remote gateways act as a digital bridge between your personal device and the hospital's secure servers.
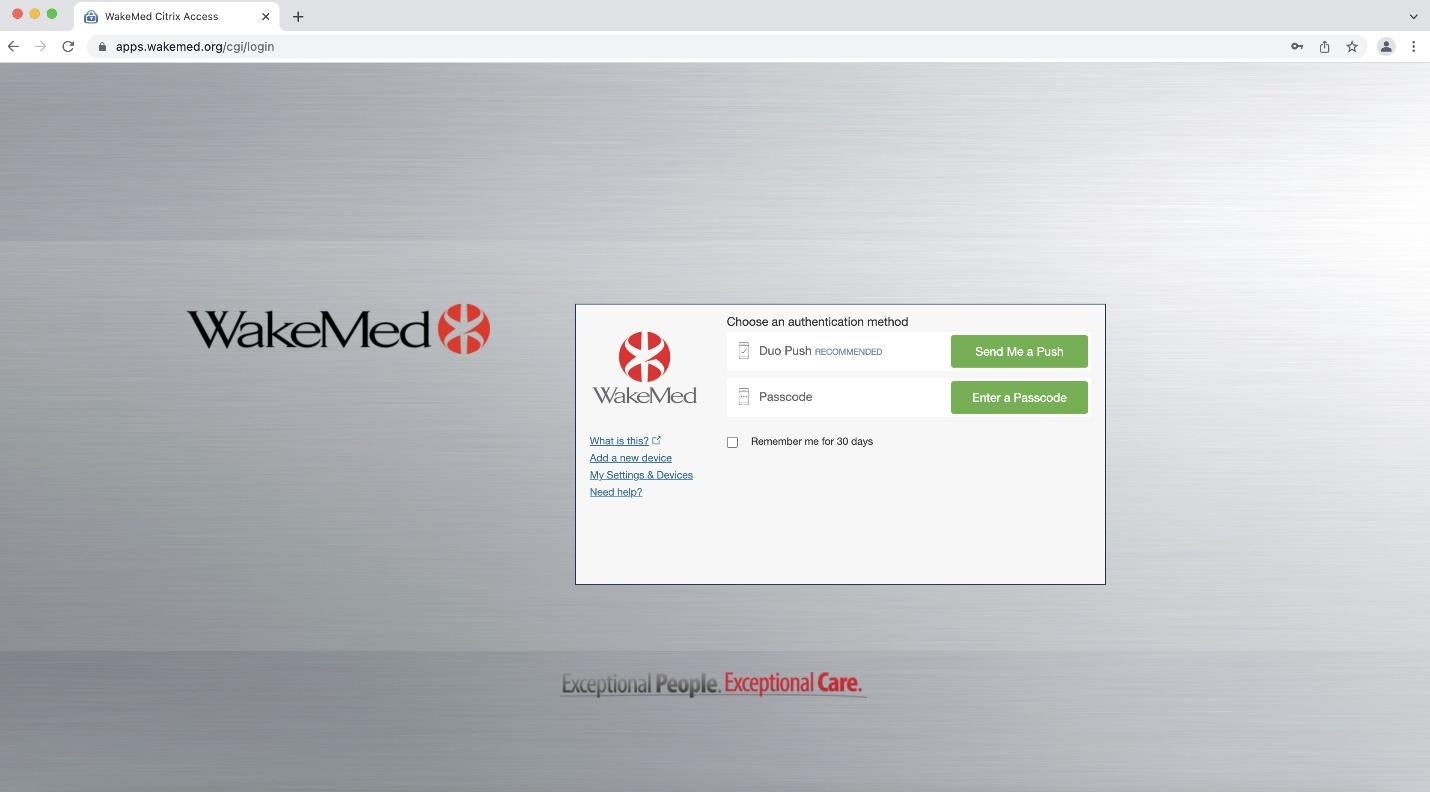
Typically, accessing these systems requires more than just a standard username and password. Healthcare networks are prime targets for malicious actors, prompting organizations to implement strict authorization protocols. While designed to keep patient data private and comply with HIPAA regulations, these tools can sometimes feel cumbersome to everyday users.
Core Components of the System
To successfully log in from an external location, the infrastructure usually relies on:
- Secure Portals: Web-based entry points that require multi-factor authentication (MFA).
- Virtual Private Networks (VPNs): Encrypted tunnels that mask data transmitted between your home Wi-Fi and WakeMed's main database.
- Endpoint Verification Software: Tools that check if your personal laptop or tablet meets minimum security standards, such as having active antivirus protection and updated operating systems.
The Benefits: Why Staff Rely on Off-Site Logins
Before weighing the cybersecurity risks, it is important to acknowledge why remote access is so heavily utilized. Healthcare does not stop at 5 PM, and administrative burdens often bleed into personal time.
Off-site connectivity allows clinicians to prepare for morning rounds the night before, review urgent test results without driving back to the hospital, and complete mandatory training modules from the comfort of home. For many employees, the flexibility prevents burnout by allowing them to balance demanding clinical hours with personal responsibilities.
The Security Risks: What Could Go Wrong?
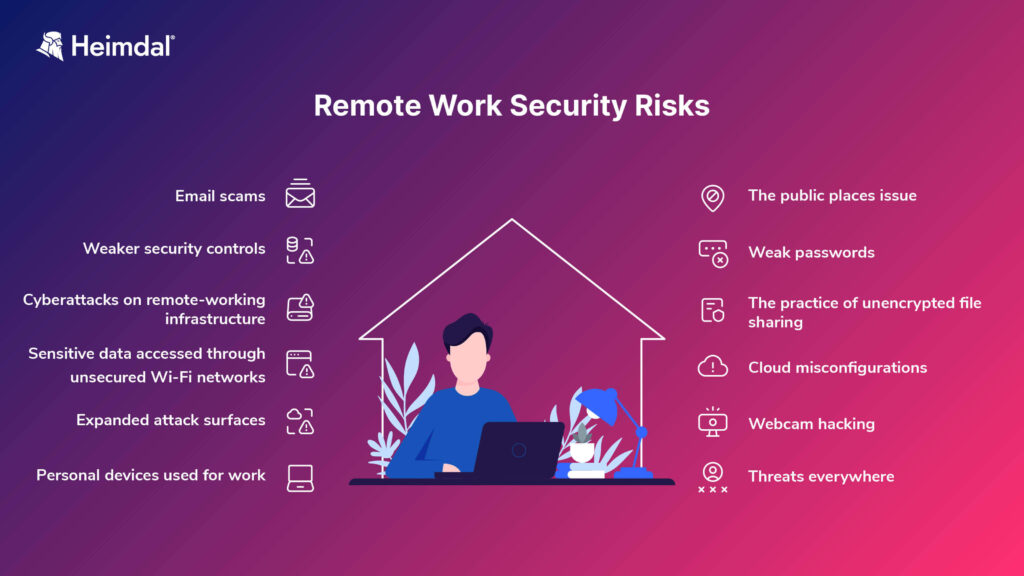
Despite the operational advantages, connecting to a major healthcare network from an external environment carries inherent dangers. Cybersecurity in medicine is a high-stakes game, and a single compromised credential can lead to disastrous consequences.
1. Phishing and Credential Harvesting
Remote workers are statistically more vulnerable to phishing attacks. Cybercriminals frequently send convincing emails designed to mimic WakeMed IT support, tricking employees into surrendering their login credentials. Once an attacker captures a valid username, password, and MFA token, they have an open door into the network.
2. Unsecured Home Networks
Hospital networks are heavily defended by enterprise-grade firewalls and monitoring teams. In contrast, a home router often uses default administrator passwords, outdated firmware, or weak Wi-Fi encryption. If a hacker breaches a home network, any device connected to it—including a laptop logged into WakeMed—could be exposed.
3. Endpoint Vulnerabilities
When staff use personal computers for work-related tasks, the risk of malware infection rises dramatically. A personal laptop might lack enterprise-grade endpoint detection and response (EDR) software, making it easier for keyloggers or ransomware to infiltrate the machine and piggyback onto the hospital network.
Weighing the Risk vs. Reward
Is using the system genuinely worth the risk? For the vast majority of users, the answer is yes—provided that strict safety protocols are followed. Hospitals cannot function in the digital age without remote connectivity, and the technology itself is not inherently flawed. The vulnerability almost always lies in human behavior and endpoint hygiene.
When security policies are respected, the risk drops significantly. However, taking shortcuts—such as saving passwords in unencrypted browsers, skipping multi-factor authentication steps, or allowing family members to use a work-connected device—tips the scale heavily toward danger.
Best Practices for Safe WakeMed Remote Access
If you need to connect to WakeMed systems from an external location, adopting rigorous digital hygiene habits is non-negotiable. Protect yourself and the institution by adhering to these guidelines:
- Never reuse passwords: Use a reputable password manager to generate and store complex, unique credentials.
- Embrace Multi-Factor Authentication (MFA): Never approve an MFA prompt on your phone unless you are actively attempting to log in. Report unexpected prompts immediately.
- Keep personal devices updated: Ensure your operating system, browser, and antivirus software are running the latest patches.
- Avoid public Wi-Fi: Never access healthcare portals using unsecured public networks at coffee shops or airports unless you are actively routing traffic through an approved corporate VPN.
- Log off completely: Always sign out of the portal and close your browser window when your work session is finished.
Conclusion
The debate surrounding remote connectivity in healthcare ultimately boils down to responsibility. While connecting to sensitive networks from outside the hospital always introduces a degree of cyber risk, it is a calculated hazard that modern medical institutions must manage. By understanding the threats, following official IT guidelines, and treating remote login credentials with extreme care, staff can safely reap the benefits of flexibility without compromising patient data or network integrity.