Why Moving Forward From Catalinasof’s Breach Feels Like a Looming Threat
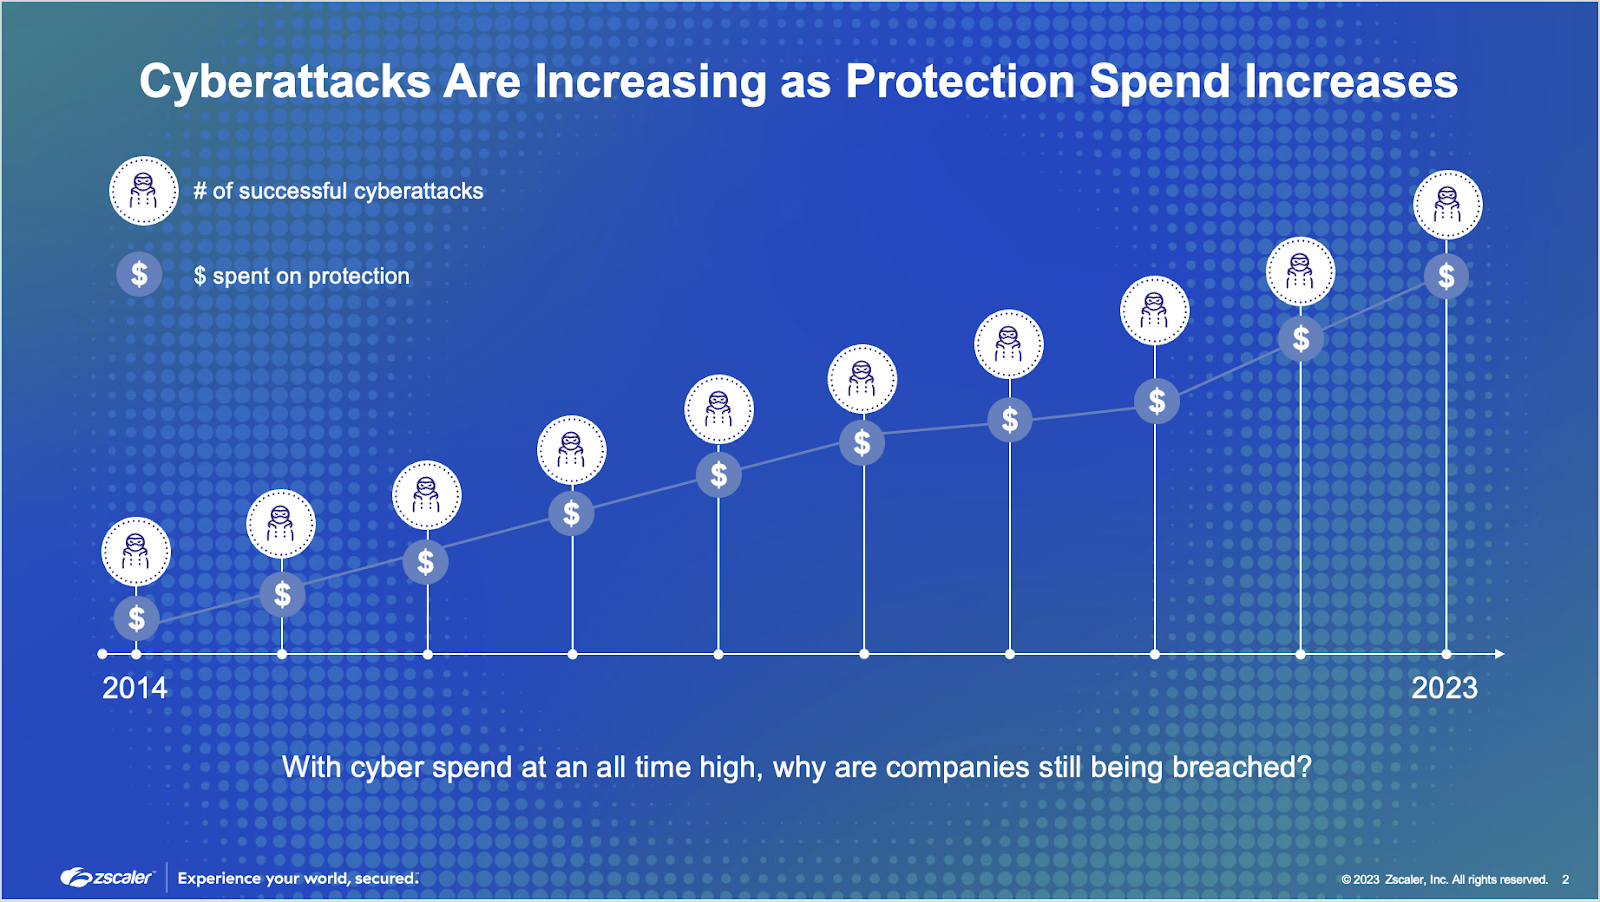
In enterprise cybersecurity, the official end of an incident response cycle rarely brings true peace of mind. System logs quiet down, indicators of compromise (IOCs) are scrubbed, and corporate communiqués assure stakeholders that the incident has been successfully contained. Yet for affected partners, security directors, and clients, why moving forward from Catalinasof’s breach feels like a looming threat comes down to a harsh reality: containment is not closure. The modern cyberattack lifecycle leaves behind invisible fractures that continue to compromise trust, data integrity, and operational security long after the initial vector is patched.

When an ecosystem anchor like Catalinasof experiences an intrusion, the fallout is rarely confined to a single database or network perimeter. Instead, the incident transforms into an ongoing operational overhang. Organizations caught in the blast radius are left grappling with systemic uncertainty, second-wave extortion threats, and the exhausting work of re-evaluating baseline operational assumptions.
The Illusion of Rapid Containment
The immediate playbook following a breach focuses on triage: isolating affected endpoints, revoking compromised service accounts, and issuing public disclosures. While these actions check compliance boxes, they often mask deeper architectural vulnerabilities.
Modern advanced persistent threat (APT) actors and sophisticated ransomware groups do not simply steal data and vanish. They establish deep persistence. When security teams move rapidly to declare an environment "clean," they risk leaving behind subtle persistence mechanisms—such as altered access controls, shadowed OAuth tokens, or backdoored build pipelines—that traditional vulnerability scanners routinely miss.
For downstream clients and integrated service providers, this creates acute anxiety. Moving forward under the assumption that systems are safe when root-cause transparency is limited feels less like operational recovery and more like walking through an active minefield.
Why Moving Forward From Catalinasof’s Breach Feels Like a Looming Threat
The lingering unease surrounding this event is rooted in tangible, compounding risks rather than vague paranoia. Organizations assessing their exposure face four structural challenges that turn standard business continuity into a high-stakes gamble.
1. The Shadow of Latent Secondary Attacks
Exfiltrated proprietary data rarely sits idle. Threat actors catalog, aggregate, and weaponize corporate data over extended timelines. Even if immediate systems are secured, stolen access logs, internal source code, and employee credentials often appear weeks or months later on dark-web forums or in targeted spear-phishing campaigns.
Downstream organizations know that an adversary possessing internal schemas or corporate communications can construct near-flawless social engineering attacks against their own staff, turning Catalinasof’s past breach into an active weapon against its perimeter.
2. Supply Chain Interdependence
Modern software architectures and enterprise service models rely heavily on interconnected APIs, shared repositories, and continuous integration/continuous deployment (CI/CD) pipelines. A vulnerability in one provider inevitably cascades across vendor ecosystems.
- API exposure: Legacy tokens or cross-tenant permissions that were not proactively revoked can grant threat actors silent read/write access.
- Data provenance questions: If database backups or shared records were tampered with during the intrusion, data integrity across downstream platforms remains questionable.
- Third-party vendor audits: Customers must now demand extensive, time-consuming compliance reassessments, straining internal resources and slowing digital transformation initiatives.
3. Regulatory and Legal Tripwires
Video: Looming Threat
Operating in the wake of a disclosed intrusion introduces acute regulatory exposure. Frameworks such as GDPR, HIPAA, and recent SEC disclosure mandates penalize not only the initial breach victim, but also business partners who fail to act decisively upon discovering potential exposure.

Moving forward requires legal and compliance officers to certify that data handling practices are secure. When forensic reports lack granular detail regarding what specific records were accessed or exfiltrated, signing off on compliance audits feels like assuming unquantified liability.
4. Internal Cognitive Fatigue and Threat Paranoia
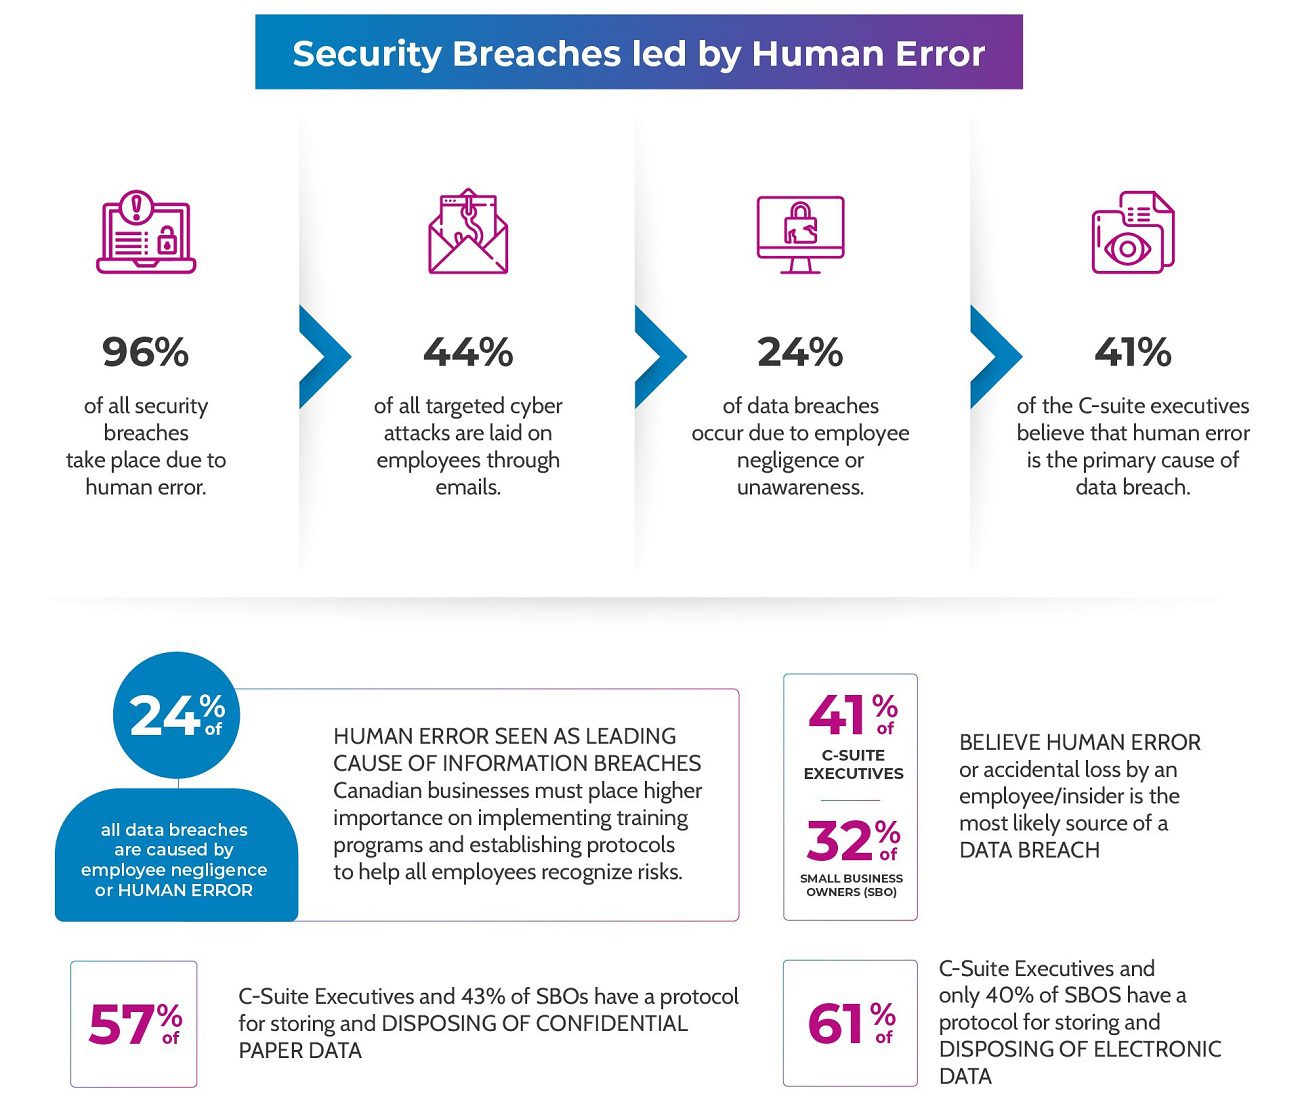
Cybersecurity operations center (SOC) analysts and infrastructure engineers bear the emotional brunt of high-profile breaches. Following an incident of this magnitude, every automated alert, unexpected failed login, or network anomaly triggers intense scrutiny.
This heightened alert state induces alert fatigue and burnout. When teams operate under chronic suspicion, their capacity to prioritize strategic engineering, system upgrades, and daily IT maintenance degrades, ironically making them more vulnerable to unrelated, mundane attack vectors.
Evaluating the Scope: What Organizations Must Audit
To replace generalized apprehension with empirical security posture management, organizations must conduct targeted investigations into their connections with Catalinasof's services. Passive monitoring is insufficient; active verification is non-negotiable.
Identity and Access Management Overhaul
The primary vector for supply chain propagation is compromised identity. Organizations should immediately assume all shared secrets and federated identity configurations were exposed during the breach window. Security teams should prioritize:
- Rotating all shared API secrets, client IDs, and webhook endpoints associated with the service.
- Enforcing strict conditional access policies, including phishing-resistant Multi-Factor Authentication (MFA) for administrative and cross-domain accounts.
- Auditing Active Directory, Entra ID, and Okta logs for anomalous lateral traversal originating from Catalinasof-linked IP ranges or service principals.
Codebase and Pipeline Sanitization
If the breach involved source-code repositories or developer dependencies, software teams must inspect build manifests. Hash verification of binary packages, software bill of materials (SBOM) comparisons, and isolated sandbox tests should be mandated before pulling software updates or integrating third-party modules into production environments.
Strategic Steps to Transition From Fear to Resilience
Accepting that risk cannot be reduced to zero is the first step toward reclaiming operational momentum. True recovery is achieved not by hoping threat actors failed to capitalize on the breach, but by constructing an architecture resilient enough to absorb potential secondary strikes.
- Adopt an Assumed-Breach Posture: Operate as though secondary threat actors already possess internal telemetry. Segment internal subnets, isolate sensitive workloads, and restrict microservice communication using Zero Trust Network Access (ZTNA) principles.
- Demand Transparent Post-Mortems: Demand detailed, cryptographically verified forensic reports rather than marketing-approved summaries. Understand exact dates of initial access, dwell time, and exfiltration techniques to align internal detection engineering accordingly.
- Conduct Focused Adversary Emulation: Engage red-team specialists to simulate attacks utilizing the specific Tactics, Techniques, and Procedures (TTPs) deployed during the Catalinasof incident. Testing real detection mechanisms under targeted stress exposes remaining gaps.
- Establish Clear Escalation Protocols: Ensure executive leadership, legal counsel, and communication teams maintain an up-to-date secondary incident response plan specifically geared toward supply-chain contagion.
Restoring Trust in an Uncertain Environment
The discomfort surrounding post-incident operations is both natural and justified. When trusted software integrations or platform vendors suffer a breach, the foundational trust underpinning modern digital workflows is broken. Yet remaining paralyzed by the possibility of future compromise is itself an operational failure.
By moving past performative reassurance and addressing the systemic, technical realities exposed by the incident, security leaders can convert justifiable dread into decisive action. Moving forward should not mean pretending the threat has vanished; it means building an enterprise resilient enough to stand firm, regardless of what the breach left behind.