Why Security Experts Restructured Safeguards After BrigotBack Leak
In the fast-evolving landscape of digital threats, certain incidents serve as watershed moments for the entire cybersecurity industry. The unauthorized exposure known as the BrigotBack leak is precisely one of those events. When proprietary security frameworks and internal communications relating to the BrigotBack architecture were suddenly dumped into the public domain, it exposed systemic blind spots that legacy defense systems simply could not handle. This Is Why Security Experts Restructured Safeguards After BrigotBack Leak incidents shattered the illusion of traditional perimeter security, prompting a massive pivot toward zero-trust architecture and continuous validation.
Anatomy of the BrigotBack Incident
To understand why security professionals reacted with such urgency, we must first examine how the breach occurred and what data was compromised. The leak did not happen overnight; rather, it was the culmination of a sophisticated, multi-stage supply chain intrusion that bypassed conventional monitoring tools.
The Vector and the Vulnerability
Attackers leveraged a combination of misconfigured cloud storage buckets and zero-day vulnerabilities within third-party vendor integrations. By exploiting these overlooked entry points, malicious actors gained persistent access to internal development repositories. They quietly harvested deployment scripts, credential vaults, and proprietary security blueprints associated with the BrigotBack ecosystem over several months before exfiltrating the data.
Immediate Industry Fallout
Once the leaked data surfaced on underground forums and public repositories, security teams scrambled to assess their own exposure. The immediate fallout included:
- Mass password resets across enterprise networks linked to similar vendor pipelines.
- Emergency patching cycles for thousands of organizations utilizing the affected software components.
- Intense regulatory scrutiny regarding third-party vendor risk management.
Why Traditional Defenses Failed
For decades, enterprise security relied heavily on the "castle-and-moat" model. This approach assumed that once a user or device successfully authenticated at the network perimeter, everything inside that network could be trusted implicitly. The BrigotBack leak brutally exposed the fatal flaw in this philosophy.
Attackers who obtained legitimate credentials could move laterally across the network completely undetected. Because legacy safeguards focused primarily on keeping unauthorized users out rather than monitoring what authenticated users were actually doing, the malicious actors operated freely within the inner sanctum. Security experts realized that perimeter defense alone was no longer viable in a world of persistent, credential-based threats.
How Security Experts Restructured Safeguards After BrigotBack Leak
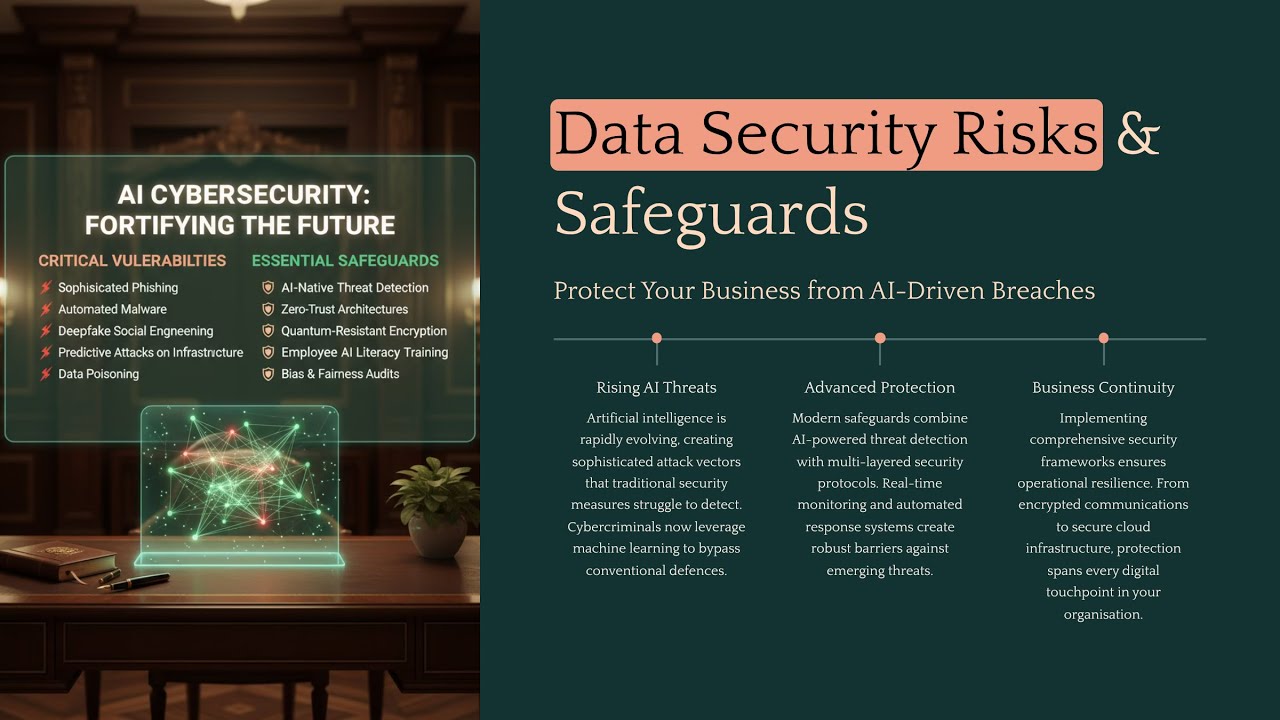
In response to the unprecedented visibility gaps exposed by the incident, cybersecurity leaders collaborated to overhaul standard operating procedures. The resulting overhaul fundamentally transformed modern security postures through several key pillars.
Adoption of Zero-Trust Architecture (ZTA)
The most profound shift following the incident was the accelerated migration toward Zero Trust. Unlike legacy models, ZTA operates on the principle of "never trust, always verify." Every single access request—regardless of whether it originates from inside or outside the corporate network—must be continuously authenticated, authorized, and encrypted before access is granted to sensitive resources.
Enhanced Supply Chain Risk Management
Because the initial breach stemmed from a third-party vendor integration, organizations could no longer treat external partners as low-risk entities. Post-leak protocols introduced stringent vendor assessment frameworks:
- Continuous automated scanning of third-party software dependencies.
- Mandatory multi-factor authentication (MFA) across all vendor portals.
- Strict principle of least privilege enforcement for external contractors.
Behavioral Analytics and Continuous Monitoring
Static signature-based detection tools proved utterly useless against the tactics used in the incident. Consequently, security teams deployed advanced Endpoint Detection and Response (EDR) solutions integrated with User and Entity Behavior Analytics (UEBA). These systems establish a baseline of normal network behavior and instantly flag anomalies, such as unusual data exfiltration patterns or unexpected credential usage, before damage can occur.
Lessons Learned for Future Defense
The aftermath of the leak serves as a permanent reminder that security is not a static destination, but an ongoing process of adaptation. Organizations that refuse to modernize their defense strategies leave themselves exposed to catastrophic operational failures.
By shifting from reactive patching to proactive threat hunting, implementing strict identity governance, and treating every network segment as potentially compromised, the cybersecurity community has built a more resilient foundation. The BrigotBack leak was painful, but it ultimately forced the industry to adopt the rigorous safeguards required to face tomorrow's threat landscape.